
Deepfake Cybersecurity Threats: Protecting Businesses From AI-Generated Fraud
Introduction
Artificial intelligence (AI) is transforming how businesses operate, communicate, and manage digital information. However, the same technology is creating new cybersecurity challenges. One of the most concerning developments is the growing misuse of deepfakes, which allow cybercriminals to create realistic images, videos, and audio recordings that impersonate real people.
For businesses across the United States, deepfake cybersecurity threats are becoming an important part of the broader fraud and identity security landscape. Criminals can clone an executive's voice, generate a convincing video of a company leader, or create fabricated communications to manipulate employees into sharing confidential information or authorizing fraudulent financial transactions.
Traditional security awareness methods are not always sufficient when attackers can imitate trusted individuals using AI-generated content. Businesses must therefore strengthen identity verification, employee awareness, financial approval procedures, and cybersecurity monitoring.
In 2026, protecting an organization requires more than conventional antivirus software and firewalls. Companies need a security strategy that addresses AI-powered impersonation, social engineering, synthetic identities, and emerging digital fraud techniques.
This article explores the major deepfake cybersecurity threats affecting businesses, their potential consequences, and practical strategies organizations can use to protect their employees, customers, and sensitive information.
1. Understanding Deepfake Cybersecurity Threats
Deepfakes are AI-generated or manipulated digital materials designed to make someone appear to say or do something that never actually happened. They can include synthetic audio, manipulated videos, fabricated images, and other forms of misleading digital content.
Cybercriminals use generative AI and machine learning technologies to produce convincing impersonations of executives, employees, customers, and public figures.
For example, an attacker may use publicly available recordings of a company executive to generate a voice message requesting an urgent payment. An employee who recognizes the voice may believe the instruction is legitimate and transfer funds without following the organization's verification process.
The FBI has warned that criminals use generative AI to improve social engineering, phishing, identity fraud, and financial scams. Its guidance also identifies AI-generated audio and video as tools used to impersonate trusted individuals. <Cite refs={["turn765385search0","turn765385search1"]}/>
The growing accessibility of AI content-generation tools makes these attacks a serious consideration for organizations of different sizes and industries.
2. Common Deepfake Attacks Targeting Businesses
Understanding how deepfake attacks work helps organizations recognize suspicious activity and strengthen their defenses.
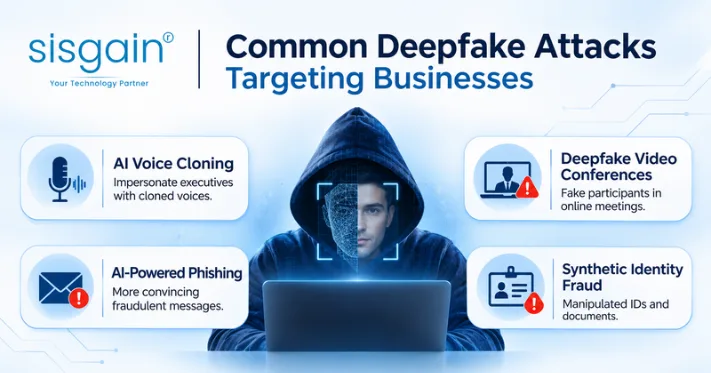
AI Voice Cloning and Executive Impersonation
Voice cloning allows attackers to imitate a person's speaking style and voice characteristics using available audio samples. Cybercriminals may use these recordings to impersonate executives, finance managers, or business partners.
For example, an employee in the finance department may receive a phone call that sounds like it comes from the company's CEO. The caller requests an urgent wire transfer or changes to supplier payment information.
Because the voice sounds familiar, the employee may feel pressured to comply.
Deepfake Video Conference Fraud
Video deepfakes can create convincing visual representations of real people. Attackers may use manipulated video during online meetings to impersonate senior executives or other authorized employees.
A fraudulent participant might request access to confidential business documents, approve a transaction, or instruct employees to disclose sensitive information.
Organizations should never treat the appearance of a person on a video call as sufficient proof of identity or authorization.
AI-Powered Phishing and Social Engineering
Traditional phishing attacks often rely on fraudulent emails and messages. Generative AI can make these communications more convincing by improving language, personalizing messages, and reproducing familiar communication styles.
Attackers may combine fabricated executive messages, realistic profile images, and cloned voices to create a coordinated impersonation attempt.
These attacks can target employees across finance, human resources, IT, customer support, and senior management.
Synthetic Identity and Document Fraud
Deepfake technology can also support identity-related fraud by creating manipulated identification images, fabricated documents, or synthetic identity materials.
Financial institutions and businesses that depend on remote identity verification may face attempts to bypass traditional authentication procedures.
The U.S. Financial Crimes Enforcement Network (FinCEN) has specifically warned financial institutions about fraud schemes involving deepfake media and manipulated identity documents.
3. Why Deepfake Attacks Are a Growing Business Risk
Deepfake attacks are particularly concerning because they exploit human trust rather than relying exclusively on technical vulnerabilities.
Employees are accustomed to receiving instructions from managers, executives, vendors, and customers. When an attacker convincingly imitates one of these individuals, the victim may overlook normal security precautions.
Several factors increase organizational exposure:
Accessible AI tools: Generative AI has made synthetic content creation easier and more widely available.
Publicly available information: Company websites, interviews, social media, and recorded meetings can provide material for impersonation.
Remote communication: Video conferencing, messaging applications, and remote approval workflows create additional opportunities for identity deception.
Human trust: Employees may act quickly when a request appears to come from someone they know.
Financial pressure: Urgent payment requests and confidential instructions can discourage employees from performing verification checks.
For U.S. businesses, these risks can affect financial operations, customer relationships, regulatory responsibilities, and organizational reputation.
4. Financial and Operational Consequences of Deepfake Fraud
A successful deepfake attack can create consequences beyond the immediate financial loss.
Financial losses: Fraudulent payment instructions, manipulated vendor communications, and executive impersonation can lead to unauthorized transfers and financial disputes.
Data exposure: Attackers may use impersonation to obtain employee credentials, customer records, internal documents, or confidential business information.
Reputational damage: Fabricated executive statements or manipulated company videos can damage customer confidence and business relationships.
Operational disruption: Organizations may need to suspend transactions, investigate suspicious communications, restore compromised accounts, and review internal security procedures.
Legal and compliance challenges: Depending on the incident and information involved, businesses may need to assess contractual obligations, applicable privacy requirements, financial reporting responsibilities, and breach notification rules.
The impact depends on the attack method, the information compromised, and how quickly the organization responds. Prevention and early detection are therefore essential parts of business continuity planning.
5. Implement Multi-Layered Identity Verification
One of the most effective ways to reduce deepfake-related fraud is to establish identity verification procedures that do not depend on a single communication channel.
For example, if a finance employee receives a voice call requesting an urgent payment, the employee should independently verify the request through an approved company communication channel.
Important security practices include:
Require multi-factor authentication for sensitive accounts.
Verify unusual payment requests through independent channels.
Establish trusted callback procedures for financial approvals.
Use approved contact directories rather than numbers supplied in unexpected messages.
Require multiple authorized approvals for high-value transactions.
Establish documented procedures for changing supplier banking details.
Businesses should also create clear escalation processes so employees can report suspicious requests without fear of delaying legitimate work.
The central principle is simple: a familiar voice, face, email address, or video call should never independently authorize a sensitive business action.
6. Strengthen Employee Awareness and Security Training
Employees are an important part of an organization's cybersecurity defense. Even sophisticated technical controls can be undermined when attackers successfully manipulate people into revealing information or approving unauthorized actions.
Businesses should provide regular security awareness training that includes practical deepfake scenarios.
Training programs should teach employees how to:
Recognize unusual communication requests.
Verify unexpected executive instructions.
Identify suspicious payment and password-reset requests.
Report potentially manipulated audio or video.
Avoid sharing confidential information through unverified channels.
Follow established approval and escalation procedures.
Organizations can also conduct controlled phishing and impersonation simulations to evaluate employee readiness.
Importantly, training should not rely entirely on identifying visual defects in deepfake videos. Modern synthetic media can be difficult to recognize, and visual or audio clues are not dependable proof of authenticity.
Independent verification procedures are more reliable than asking employees to guess whether a recording is genuine.
7. Use AI-Powered Cybersecurity and Deepfake Detection Tools
AI can be used by attackers, but it can also support defensive security operations.
Modern cybersecurity solutions may use machine learning, behavioral analytics, anomaly detection, and identity verification technologies to identify suspicious activity.
Potential applications include:
Deepfake media analysis: Specialized tools can examine audio and video characteristics for signs of manipulation.
Behavioral monitoring: Security platforms can identify unusual login patterns, unexpected access requests, and suspicious account activity.
Email threat detection: AI-assisted security tools can analyze message content, sender behavior, links, and attachments to identify potential phishing attempts.
Identity verification: Organizations can combine document verification, authentication signals, and liveness checks to strengthen remote identity processes.
However, detection technologies are not completely reliable. A detection score should not be treated as conclusive proof that media is authentic or manipulated.
Businesses should combine technical detection with independent identity checks, human review, and documented security procedures.
8. Protect Sensitive Data and Strengthen Access Controls
Deepfake fraud often works alongside other cyberattack techniques. An impersonation attempt may be the first step toward obtaining credentials, accessing business applications, or extracting confidential information.
Organizations should therefore maintain strong access control and data protection practices.
Important measures include:
Apply role-based access controls.
Require multi-factor authentication.
Encrypt sensitive information during storage and transmission.
Monitor privileged accounts and unusual access patterns.
Regularly update operating systems and business applications.
Maintain secure backups and recovery procedures.
Review employee and third-party access permissions.
A zero-trust security approach can provide an additional layer of protection by requiring continuous verification of users, devices, and access requests rather than automatically trusting activity within a corporate network.
9. Develop a Deepfake Incident Response Plan
Even organizations with strong cybersecurity controls may experience attempted impersonation or fraud. A documented incident response plan helps employees understand what to do when suspicious activity occurs.
A practical response process should include:
Identify: Recognize and report suspicious audio, video, messages, or payment instructions.
Verify: Contact the alleged sender through an independently established communication channel.
Contain: Suspend suspicious transactions and restrict potentially compromised accounts.
Investigate: Review relevant emails, access logs, payment records, and communication histories.
Recover: Reset compromised credentials, restore affected systems, and verify account integrity.
Improve: Document lessons learned and update security controls and employee training.
Organizations should also identify the appropriate internal security contacts, financial institutions, legal advisers, and external authorities for incident escalation.
In the United States, businesses affected by suspected cyber-enabled financial fraud can consider reporting relevant incidents to the FBI's Internet Crime Complaint Center (IC3).
10. Choosing the Right Cybersecurity Partner
Building an effective deepfake defense strategy requires a combination of technology, operational processes, and cybersecurity expertise.
Businesses should evaluate providers based on their ability to understand organizational risks and develop security measures that match specific business requirements.
When comparing cybersecurity solutions dubai, organizations should consider the provider's experience in identity security, threat detection, endpoint protection, cloud security, and incident response.
A reliable cybersecurity solution dubai should also support security assessments, access management, employee awareness, and ongoing vulnerability monitoring.
Businesses evaluating a cybersecurity solutions provider dubai should review its technical capabilities, service-level commitments, implementation approach, and experience handling modern AI-enabled threats.
For U.S. organizations working with international cybersecurity partners, it is especially important to confirm that services align with their operating environment, contractual responsibilities, applicable regulations, and data protection requirements.
The right cybersecurity partner should offer practical protection strategies rather than relying on generic technology recommendations.
Contact SISGAIN Technologies today! for reliable cybersecurity solutions tailored to your business needs.
Conclusion
Deepfake cybersecurity threats are changing how businesses must approach digital identity, financial security, and employee verification. AI-generated voices, manipulated videos, synthetic identities, and personalized phishing campaigns can make fraudulent communications appear increasingly trustworthy.
For businesses across the United States, addressing these risks requires a proactive and layered security strategy. Multi-factor authentication, independent identity verification, employee training, AI-assisted threat detection, secure access controls, and incident response planning all play important roles.
Organizations should also recognize that no single detection tool can prevent every deepfake attack. Combining technology with reliable business processes and human oversight creates a stronger defense.
As AI capabilities continue to evolve in 2026, businesses that prioritize identity verification and cybersecurity awareness will be better positioned to protect their financial assets, sensitive information, employees, and customer trust.
0 comments
Log in to leave a comment.
Be the first to comment.