
Why WordPress Malware Keeps Coming Back After Cleanup: Understanding Reinfection
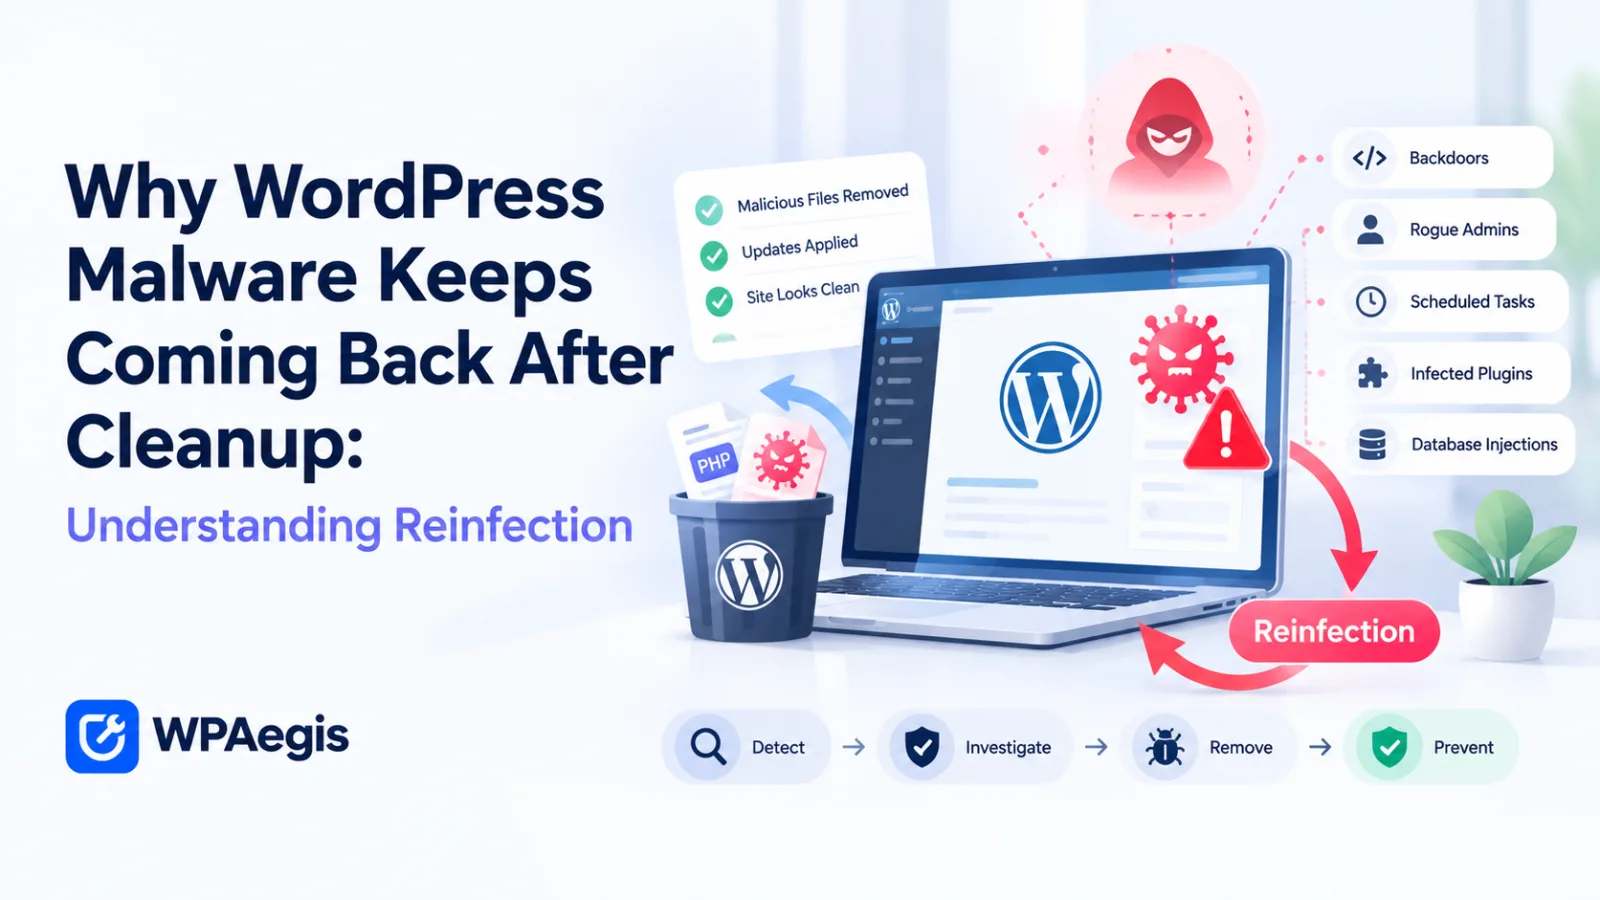
Removing visible malware from a WordPress website does not necessarily mean the infection is gone.
A site can look completely normal after suspicious files are deleted, passwords are changed, and a security scan reports no obvious threats—yet become infected again hours or days later.
The reason is usually persistence.
Attackers may leave behind a backdoor, unauthorized administrator account, malicious scheduled task, modified plugin, database payload, or hidden PHP file that can restore the infection after cleanup.
This is why effective malware cleanup should focus on both removing the current infection and eliminating the mechanism that allows it to return.
For businesses that depend on WordPress availability and trust, WPAegis approaches website security as an ongoing operational concern rather than treating malware as a one-time file deletion problem.
What Is WordPress Malware Reinfection?
WordPress malware reinfection occurs when malicious code returns after a website has already been cleaned.
There are several possible explanations:
A hidden backdoor was not removed.
A compromised administrator account still exists.
A malicious plugin or theme remains installed.
A scheduled task restores the malware.
The database still contains malicious code.
A configuration file was modified.
Stolen credentials allow the attacker to regain access.
A compromised hosting environment affects the website again.
A vulnerable component provides the original entry point again.
In other words, deleting the infected file is only one part of the cleanup process.
The more important question is:
What allowed the attacker to put the malware there in the first place, and what mechanism could put it back?
1. Hidden Backdoors Can Survive the Initial Cleanup
A backdoor gives an attacker a way to access a website without using the normal WordPress login process.
For example, a malicious PHP file could accept a specially crafted request and execute code on the server.
The file might have an innocent-looking name and be located somewhere administrators rarely inspect.
Common locations that deserve investigation include:
wp-content/uploads/wp-content/mu-plugins/plugin directories
theme directories
WordPress configuration files
unfamiliar PHP files
modified core files
server configuration files
The dangerous part is that a backdoor may not cause an obvious visible problem.
The website may load normally while the attacker retains access in the background.
That is why a successful malware cleanup should include a search for persistence mechanisms, not just recognizable malware signatures.
2. Must-Use Plugins Can Be Easy to Overlook
WordPress has a special mechanism called must-use plugins, commonly stored in wp-content/mu-plugins/.
Unlike normal plugins, must-use plugins are automatically loaded and do not appear in the standard Plugins screen in the same way. WordPress documentation explains that they cannot simply be disabled from the normal WordPress administration interface.
This makes them useful for legitimate hosting, security, and site-specific functionality.
It also means administrators should not ignore this directory during an investigation.
A suspicious PHP file inside mu-plugins may continue executing even after obvious infected plugins have been removed.
Therefore, during a malware investigation, every must-use plugin should be:
Identified.
Verified.
Connected to a legitimate purpose.
Checked for unexpected modifications.
Removed or replaced if its origin cannot be trusted.
Do not automatically delete every mu-plugin, however. Hosting platforms and legitimate site configurations may use them.
The goal is verification, not indiscriminate deletion.
3. Rogue Administrator Accounts Can Restore Access
Attackers sometimes create additional administrator accounts after compromising a website.
The account may use:
A random username
A fake business identity
A legitimate-looking email address
A username resembling WordPress system accounts
An account that is hidden or difficult to notice
Deleting the malicious files while leaving an attacker-controlled administrator account creates an obvious recovery path.
The attacker may simply log in again and upload another payload.
A proper investigation should therefore review:
All administrator accounts
Usernames
Email addresses
Account creation dates
Recent login activity
User roles
Unknown application passwords
Session information
Changes to user capabilities
A useful question is:
Does every administrator account have a documented owner and legitimate reason to exist?
If the answer is no, investigate before trusting the site again.
4. WP-Cron Can Become a Persistence Mechanism
WordPress uses scheduled events for many normal tasks.
WP-Cron can trigger actions such as publishing scheduled content, processing plugin tasks, and running other scheduled events. WordPress documentation also explains that WP-Cron relies on loopback requests to execute scheduled events.
That functionality can become dangerous when an attacker creates or abuses a malicious scheduled event.
For example, a compromised site could contain a scheduled task designed to:
Download another payload
Recreate a deleted file
Contact an external server
Modify database content
Create another administrator
Restore a deleted backdoor
This creates a frustrating cycle:
Clean file → malicious task runs → file returns → site becomes infected again
Therefore, malware investigations should include a review of scheduled tasks rather than focusing exclusively on the filesystem.
5. The Database Can Keep the Infection Alive
Not all malware lives inside PHP files.
Attackers can also inject malicious content into the WordPress database.
Potential locations include:
wp_optionsPosts
Pages
Post metadata
User metadata
Widget settings
Plugin configuration
Serialized settings
Custom tables
Database malware can be particularly difficult to notice because the website may continue functioning normally.
An attacker might insert:
JavaScript
Hidden links
Spam content
Redirect instructions
Encoded payloads
Malicious administrator settings
Persistent configuration values
This is why a file-only cleanup may fail.
A complete investigation should consider files, database records, users, scheduled tasks, and configuration together.
6. Modified Plugins and Themes Can Reintroduce the Infection
A compromised plugin or theme can act as the mechanism that restores malware.
Imagine this sequence:
Website is infected.
Malware scanner identifies several suspicious PHP files.
Administrator deletes those files.
The compromised plugin remains.
The plugin executes again.
Deleted malware is recreated.
The administrator may think the cleanup failed randomly.
In reality, the persistence mechanism was never removed.
WordPress's plugin ecosystem also demonstrates why supply-chain security matters. WordPress.org now subjects new plugin releases to automated security review before distribution through its update API, with high-risk releases potentially blocked.
This does not eliminate every risk, particularly for third-party plugins, abandoned software, modified packages, or compromised credentials.
Plugin and theme integrity therefore remains an important part of malware investigations.
7. Stolen Credentials Can Make a Clean Website Vulnerable Again
Sometimes the malware itself is not the reason for reinfection.
The attacker may still have valid credentials.
Potentially compromised credentials include:
WordPress administrator passwords
Hosting accounts
FTP/SFTP credentials
Database credentials
SSH accounts
Control-panel logins
API keys
Application passwords
Changing only the WordPress administrator password may not be enough.
If the attacker obtained hosting or database credentials, they may be able to modify the website without using WordPress authentication.
A serious compromise should therefore trigger a credential review across the entire hosting stack.
8. Why Reinstalling WordPress Sometimes Isn't Enough
Replacing WordPress core files can be an important step, but it does not automatically clean everything.
An infection can exist outside the standard core directories.
For example:
Core files
→ wp-admin
→ wp-includes
Site-specific components
→ plugins
→ themes
→ uploads
→ mu-plugins
Persistent data
→ database
→ scheduled tasks
→ administrator accounts
→ configuration files
Hosting layer
→ control panel
→ FTP/SFTP
→ server configuration
→ other websites on the same account
Replacing only WordPress core leaves many potential persistence locations untouched.
9. Why a Clean Backup Can Be Better Than Repeated Manual Deletion
If the infection is extensive, repeatedly deleting suspicious files may create an endless cleanup cycle.
A safer recovery strategy can involve:
Identifying when the compromise occurred.
Finding a trustworthy pre-infection backup.
Validating the backup.
Rebuilding from clean WordPress files.
Reinstalling trusted plugins and themes.
Reviewing the database.
Removing unauthorized accounts.
Rotating credentials.
Checking configuration files.
Scanning the rebuilt environment.
Monitoring the website after restoration.
However, backups should not automatically be considered clean.
If the backup was created after the infection began, restoring it may simply restore the malware.
The objective is not merely "restore an old version."
The objective is:
Restore a version that can be reasonably trusted.
10. Malware Removal Should Include the Root Cause
A malware removal process should answer three separate questions:
What Is Infected?
Identify malicious files, database injections, unauthorized users, suspicious plugins, altered configurations, and other indicators.
How Did the Attacker Get In?
Possible entry points include:
Vulnerable plugins
Vulnerable themes
Outdated WordPress components
Stolen credentials
Weak authentication
Hosting-level compromise
Malicious third-party software
How Could the Attacker Get Back In?
This is the most frequently overlooked question.
If the answer is still "yes," the cleanup is incomplete.
For businesses dealing with persistent infections, WPAegis Malware Removal can be relevant when the problem requires more than simply deleting a suspicious file.
11. What a Proper WordPress Malware Cleanup Should Check
A thorough investigation should cover multiple layers.
Filesystem
Check:
WordPress core
Plugins
Themes
Uploads
mu-pluginsDrop-ins
Configuration files
Unexpected PHP files
Database
Review:
Administrator records
User metadata
Options
Posts and pages
Suspicious serialized data
Injected scripts
Unknown database tables
Accounts
Review:
Administrators
Editors
Application passwords
Hosting users
FTP/SFTP accounts
API credentials
Scheduled Execution
Inspect:
WP-Cron events
Server cron jobs
Scheduled scripts
Unexpected automation
Configuration
Check:
wp-config.php.htaccess.user.iniPHP configuration
Redirect rules
Server-level settings
External Access
Investigate:
Suspicious outbound connections
Unknown APIs
Remote payload downloads
Unexpected domains
Webhooks or integrations
The more persistent the infection, the more important this layered approach becomes.
12. How to Prevent WordPress Malware From Returning
After cleanup, prevention should become an ongoing process.
Keep WordPress Components Updated
Old software can contain known vulnerabilities.
Maintain:
WordPress core
Plugins
Themes
Server software
PHP versions
But do not update blindly on a production website without considering compatibility and recovery options.
Remove Unused Plugins and Themes
Unused software increases the amount of code that must be trusted and maintained.
If a plugin is not required, removing it can reduce the attack surface.
Protect Administrator Accounts
Use:
Strong unique passwords
Two-factor authentication
Least-privilege roles
Limited administrator access
Regular account reviews
Maintain Reliable Backups
A backup is only useful if:
It actually exists.
It can be restored.
It is recent enough.
It is stored separately from the website.
It has not been compromised.
Test restoration periodically instead of assuming backups work.
Monitor After Cleanup
The period immediately after remediation matters.
Look for:
New files
Unexpected administrator accounts
Reappearing malware
Configuration changes
Suspicious redirects
Unusual server activity
Unexpected scheduled tasks
A clean scan immediately after cleanup is useful, but it does not prove that the website will remain clean indefinitely.
WordPress Malware Cleanup vs. Malware Prevention
These are related but different activities.
Malware CleanupMalware PreventionRemoves existing infectionReduces future riskInvestigates persistenceMonitors for changesRemoves backdoorsControls accessRestores compromised filesKeeps software updatedReviews attacker accessProtects administrator accountsChecks database contaminationMaintains reliable backupsA website can be clean today and still become vulnerable tomorrow.
That is why malware remediation and ongoing security should be treated as separate but connected processes.
Frequently Asked Questions
Can WordPress Malware Come Back After Cleanup?
Yes. Reinfection can happen when a backdoor, compromised account, malicious scheduled task, infected plugin, database payload, or other persistence mechanism remains.
Why Does Malware Return After I Delete the Infected Files?
The deleted file may not be the source of the infection. Another component may recreate it. Recent WordPress support reports demonstrate how persistent infections can involve multiple files, database entries, scheduled tasks, and unauthorized accounts.
Should I Delete Everything in the WordPress Uploads Folder?
No. The uploads directory can contain legitimate media and other site files. Instead, investigate suspicious files carefully and determine whether they belong there.
Can a WordPress Plugin Cause Reinfection?
Yes. A compromised or malicious plugin can potentially provide persistence or recreate malicious files. However, the presence of a suspicious plugin does not automatically prove that it was the original entry point.
Does Changing My WordPress Password Stop Malware?
Not necessarily. Password changes can help invalidate compromised credentials, but they do not remove malicious code or other persistence mechanisms.
Should I Restore a Backup After a WordPress Hack?
A verified clean backup can be an effective recovery option. However, restoring a backup created after the compromise may restore the infection as well.
How Do I Know Whether WordPress Malware Has Been Completely Removed?
There is no single test that guarantees permanent cleanliness. Confidence improves when the site is rebuilt or cleaned comprehensively, persistence mechanisms are removed, credentials are rotated, software is updated, and the website is monitored afterward.
Final Thoughts
WordPress malware removal should not end when the suspicious PHP file disappears.
The real objective is to eliminate the entire infection chain.
That means investigating how the attacker entered, what access they obtained, what persistence mechanisms were installed, whether the database was modified, whether credentials were compromised, and whether anything remains capable of recreating the malware.
A website that looks clean but still contains a backdoor is not actually clean.
The strongest recovery strategy combines malware removal, root-cause investigation, credential protection, software integrity, trusted backups, and post-cleanup monitoring.
That approach turns malware cleanup from a temporary fix into a proper recovery process.
0 comments
Log in to leave a comment.
Be the first to comment.