
Why "Hosted in India" Isn't the Same as "Data Sovereign"
Next time a cloud vendor tells you "your data stays in India," try this. Ask one follow-up: if a court in another country ordered you to hand over my data, would you have to?
A good vendor answers that straight. A less good one goes back to talking about their Mumbai data centre, which is a different question altogether.
That mix-up is what I want to untangle here. "Where does my data sit" and "who can be made to hand it over" sound like one question. They are two. One is about a building. The other is about who the company answers to. Most compliance checklists only ask the first, and that is how teams end up feeling covered when they are not.
What Is the Difference Between Data Residency and Data Sovereignty?
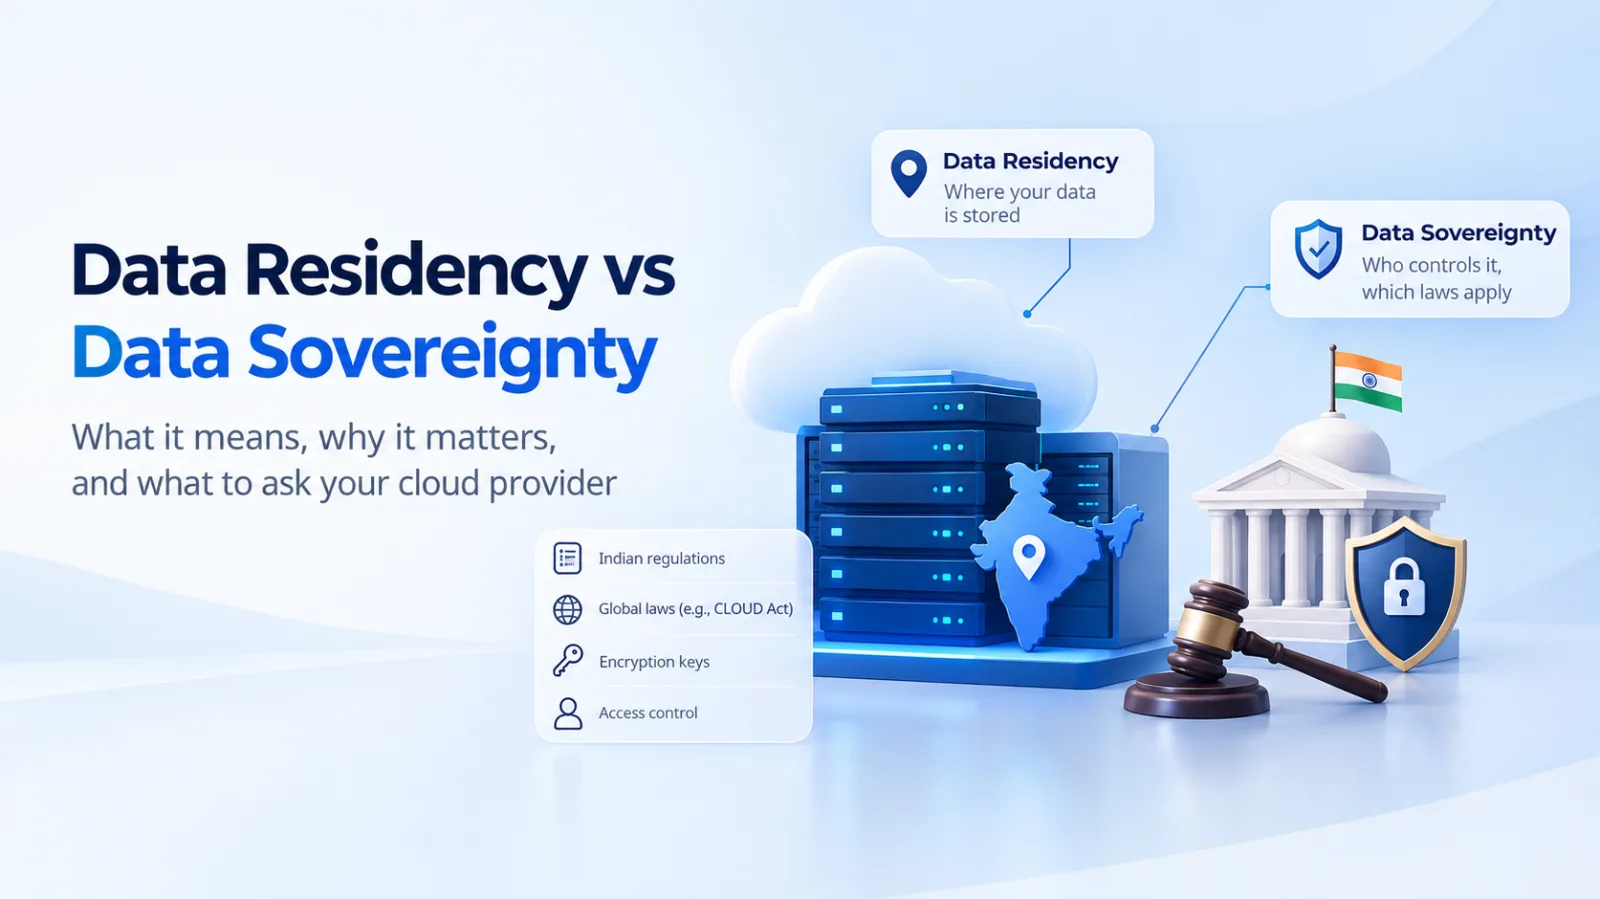
Data residency is about location. It tells you where your data is physically stored. Data sovereignty is about control. It tells you whose laws govern the data, who can legally compel access to it, and who holds the encryption keys.
A server can sit in Mumbai and still be answerable to a law written in another country. That gap is the whole point of this article.
Why Do People Mix These up so Often?
Because "hosted in India" is easy to say and easy to verify, while control is hard to explain and harder to check. It fits neatly on a pricing page. A sentence about corporate jurisdiction and key management does not.
Can a Foreign Government Still Access Data Stored in an Indian Data Centre?
In some cases, yes. The US CLOUD Act is the usual example. It applies based on who controls the data, not where the servers are. A provider incorporated in the United States can be required to hand over data it controls, even if that data sits in an Indian region.
Legal commentators have also pointed out that India has no executive agreement under the CLOUD Act. That means there is no treaty route for challenging such a request through Indian courts.
Does This Mean Using a Global Cloud in India Is Unsafe or Illegal?
No, and I want to be clear about that. For most workloads, a global provider's Indian region is a perfectly reasonable choice. The concern is specific to sensitive data and regulated sectors, not every app and every dataset. Treat this as a risk to size, not a reason to panic.
What Does Indian Law Actually Require Today?
Less than people assume, at least at the general level. The DPDP Act uses a negative list model. Personal data can move outside India unless the government restricts a specific destination or category.
The hard rules sit in sector regulation. The DPDP Act also says stricter laws in other sectors continue to apply, so those rules win where they exist.
Is MeitY Empanelment the Same as Being Sovereign?
No. Empanelment shows a provider has gone through an audit for security and compliance. It is not a sovereignty certification. Treating it as one is the same mistake as treating "hosted in India" as proof of sovereignty, just with an official stamp on it.
What Should You Ask a Cloud Provider to Check Real Sovereignty?
Five questions will tell you more than any brochure.
Who owns and controls the company? Look at where it is incorporated and who its parent is, not just where its data centres are
Who holds the encryption keys? Ask whether you can bring your own keys, and whether the provider can ever access them
Where are the people with admin access? Support staff and engineers working from other countries can change the risk picture
What does the contract say about government requests? Check whether the provider commits to notifying you and to pushing back where it legally can
Where do backups, logs and metadata go? Your main database may stay put while supporting data quietly moves elsewhere
Do You Need to Run This Full Check for Every Workload?
No. Match the effort to the data. A public dataset or a test environment does not need the same scrutiny as customer financial records or health data. Sort your workloads by sensitivity first, then apply the full check only where it actually matters.
What Does This Look Like in a Real Situation?
Picture a fintech startup that stores customer KYC records with a global cloud provider, in its Mumbai region. The data never leaves India, so on paper everything looks fine. Then an enterprise customer sends a security questionnaire asking who can access the data, under which country's laws, and who manages the encryption keys.
If the team cannot answer, the deal stalls. Nothing was technically broken. They simply solved for location and never thought about control.
The fix is rarely dramatic. Usually it means moving key management into the team's own hands, writing down the access policy, and picking a provider who can answer those questions in plain language. Doing that before a customer asks is far cheaper than doing it after.
A Few Quick Questions People Keep Asking About This
Is hosting in an Indian data centre enough to comply with the DPDP Act? For general personal data, the DPDP Act does not force you to keep everything in India. Residency alone does not cover sector rules, though, so check what your regulator requires on top.
Does choosing an Indian provider automatically give me data sovereignty? Not automatically. Ownership, investors, key management, subprocessors and support locations all still matter. An Indian address on the invoice is a good start, not a finished answer.
Can encryption solve this on its own? It helps a lot, especially when you hold the keys yourself. It does not cover everything, since metadata and key management arrangements can still create exposure. Think of it as one strong layer, not the whole wall.
Where This Leaves You
"Hosted in India" is a useful fact, and for many workloads it is all you need. But it describes location, and sovereignty is about control. If your data is regulated, sensitive, or tied to customers who will ask hard questions, look past the data centre address and ask who actually holds the keys and whose laws apply.
This is general information, not legal advice. For anything tied to a specific regulator, a short conversation with a lawyer who knows your sector is worth the time.
0 comments
Log in to leave a comment.
Be the first to comment.