
NESA Compliance UAE: Protect Your Business With SecureSist

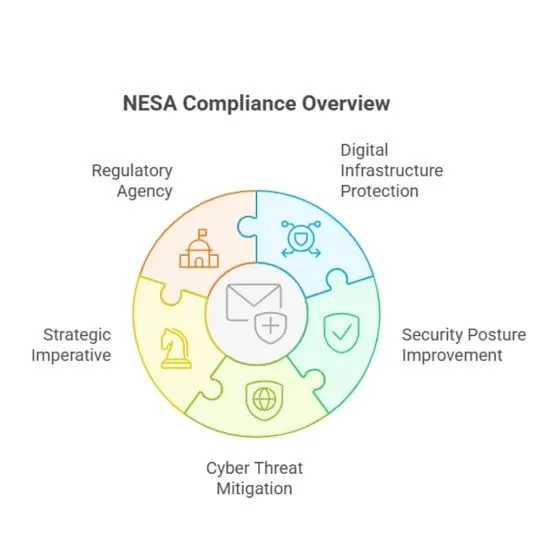
Businesses in the UAE must take cybersecurity seriously. Protecting company data, networks, and digital systems is important for business continuity and customer trust. For organizations working with government entities or critical sectors, meeting the right security requirements is even more important.
NESA compliance UAE is a key search term for organizations looking for guidance on national cybersecurity requirements and security controls. Businesses need to understand which rules apply to them, assess their current security measures, and address any gaps.
SecureSist helps organizations explore cybersecurity and information security needs. If your business needs support with security assessments, compliance planning, or risk management, working with an experienced cybersecurity provider can help you take a structured approach.
Whether you operate in Dubai or elsewhere in the UAE, the first step is to understand your obligations and build a security plan that fits your organization.
What Is NESA Compliance in the UAE?
Understand the cybersecurity requirements that apply to your organization.
Review security policies and technical controls.
Identify risks to business systems and sensitive data.
Address gaps in security and compliance.
Maintain records of security measures and improvements.
NESA refers to the UAE's former National Electronic Security Authority. Its cybersecurity standards helped establish security requirements for important information systems in the country.
The UAE's cybersecurity framework has evolved, and organizations should verify the current authority, standards, and requirements that apply to their sector. In particular, the UAE's National Cybersecurity Council now plays a central role in national cybersecurity coordination.
When businesses search for NESA compliance UAE, they are often looking for help understanding applicable cybersecurity controls, preparing for assessments, and improving their security posture.
Compliance is not simply about completing documents. It also involves putting suitable controls in place, checking that they work, and reviewing them as business risks change.
Why Is NESA Compliance Important for UAE Businesses?
Helps identify cybersecurity weaknesses.
Supports better protection of sensitive information.
Improves awareness of security responsibilities.
Helps organizations prepare for relevant assessments.
Supports business continuity and risk management.
Cyber threats can affect organizations of every size. Weak passwords, outdated software, poor access controls, and limited employee awareness can expose systems to unnecessary risks.
A structured compliance program helps businesses review these areas and decide which improvements matter most. It can also help management understand security responsibilities and allocate resources more effectively.
For organizations in regulated or critical sectors, meeting applicable cybersecurity requirements may be a formal obligation. Other businesses may need to meet security expectations set by customers, partners, or contracts.
SecureSist can be contacted to discuss your organization's cybersecurity and compliance needs. Your team should first confirm which framework and controls apply to your business before starting a compliance project.
Key Areas to Review for NESA Compliance UAE
Risk management: Identify important assets, threats, and possible business impacts.
Access control: Limit system access to authorized users.
Data protection: Protect sensitive information from unauthorized access.
Network security: Review firewalls, network access, and monitoring.
Incident response: Prepare a clear process for handling security incidents.
Business continuity: Plan how to maintain or restore essential services.
Security awareness: Train employees to recognize common cyber threats.
A practical NESA compliance UAE program starts with a review of the organization's existing security controls.
The assessment should consider how information is stored, who can access it, how systems are monitored, and what happens when a security incident occurs.
Documentation is also important. Policies, risk assessments, access records, incident procedures, and evidence of control testing can help demonstrate how security is managed.
The exact controls depend on the applicable framework, industry, system classification, and regulatory obligations. Businesses should avoid assuming that one checklist is suitable for every organization.
NESA Compliance Assessment and Gap Analysis
Review current cybersecurity policies and procedures.
Identify applicable standards and requirements.
Assess existing technical and organizational controls.
Record gaps and areas of concern.
Prioritize corrective actions.
Track improvements and maintain evidence.
A gap analysis compares your current security practices with the requirements that apply to your organization. It helps identify what is already in place and what needs attention.
For example, a company may have an access control policy but lack regular access reviews. Another organization may use security software but have no documented incident response procedure.
A structured assessment helps turn these findings into clear actions. Each issue can be assigned a priority, responsible person, and target completion date.
Organizations seeking cybersecurity compliance services UAE should ask providers how they assess controls, document findings, and help teams plan corrective actions.
SecureSist can be contacted to discuss your requirements and determine whether its current services match your assessment and compliance needs.
How to Prepare for a Cybersecurity Compliance Review
Identify the systems and data that need protection.
Confirm the relevant regulatory requirements.
Gather existing policies and security records.
Review user permissions and system access.
Check backup and incident response procedures.
Document gaps and assign corrective actions.
Schedule regular reviews and updates.
Preparation makes compliance reviews more organized. It also helps reduce the time spent searching for policies, technical records, and evidence during an assessment.
Start by assigning responsibility for the process. Your IT team, management, compliance staff, and external advisers may all need to contribute.
Next, create a clear record of the controls already in place. Include evidence such as approved policies, access reviews, backup tests, security awareness records, and incident response exercises where relevant.
For businesses seeking information security compliance UAE, regular monitoring is just as important as the initial review. Security controls can become outdated when systems, staff, suppliers, or business operations change.
A planned review cycle helps keep documentation accurate and security measures aligned with current needs.
Why Consider SecureSist for Compliance Support?
A direct contact point for cybersecurity enquiries.
An opportunity to discuss security risks and compliance goals.
Support in understanding your organization's requirements.
A starting point for exploring suitable security services.
Choosing a cybersecurity provider requires careful review. Before engaging a company, confirm its experience with your industry, knowledge of the relevant framework, assessment methods, and ability to provide clear documentation.
Ask whether the service includes a gap assessment, remediation guidance, policy review, technical testing, or ongoing support. These services are different, so make sure the proposed scope matches your needs.
SecureSist serves as a contact for organizations exploring cybersecurity services in the UAE and Dubai, as well as Egypt. Contact the team to confirm its current service offering and experience with the specific compliance framework your organization must follow.
No provider should promise compliance without reviewing your systems and requirements. The final outcome depends on the controls implemented by your organization and the applicable assessment process.
Frequently Asked Questions
What Does NESA Compliance Mean in the UAE?
It commonly refers to cybersecurity requirements associated with the former NESA framework.
It involves reviewing security risks, controls, and supporting evidence.
Organizations should confirm which current standards and rules apply to them.
The exact obligations vary by sector and organization.
Is NESA Compliance Mandatory for Every UAE Business?
Not every business has the same obligations.
Requirements may depend on the sector and systems involved.
Contracts and regulatory rules may create additional security requirements.
Check with the relevant authority or a qualified compliance adviser before deciding which framework applies.
How Can a Business Prepare for NESA Compliance UAE?
Identify applicable requirements.
Assess existing cybersecurity controls.
Document gaps and risks.
Implement corrective actions.
Keep evidence of ongoing reviews.
A structured plan helps teams manage the process more effectively.
What Is Included in a Cybersecurity Compliance Assessment?
Review of policies and procedures.
Assessment of technical security controls.
Risk and gap analysis.
Documentation of findings.
Recommendations for corrective action.
The scope depends on the framework and the organization's requirements.
How Can I Contact SecureSist?
You can contact SecureSist to discuss your cybersecurity and compliance requirements.
Company: SecureSist
Email: [email protected]
Phone: +971 56 896 6556
Alternative phone: +971 50 317 4898
Website: https://securesist.com/
Service locations provided: UAE, Dubai, and Egypt
Contact SecureSist to Discuss Your Compliance Needs
Meeting cybersecurity requirements starts with understanding your risks, identifying the right framework, and taking clear steps to address security gaps.
If you are researching NESA compliance UAE, begin by reviewing your current controls and confirming the obligations that apply to your organization.
SecureSist can be contacted to discuss your needs and explore suitable cybersecurity support.
Email [email protected] or call +971 56 896 6556 / +971 50 317 4898 to make an enquiry. Visit securesist.com for more information.
phishing protection
security awareness training
Domain Protection
Executive Protection
ISO 27001 certification Dubai
attack surface monitoring
phishing simulation
0 comments
Log in to leave a comment.
Be the first to comment.