
Master Network Security and SOC Fundamentals – AI Cyber Security Course in Telugu With Networking & SOC
Understanding how networks communicate and how security teams investigate suspicious activity can help beginners build a foundation for a cybersecurity career.
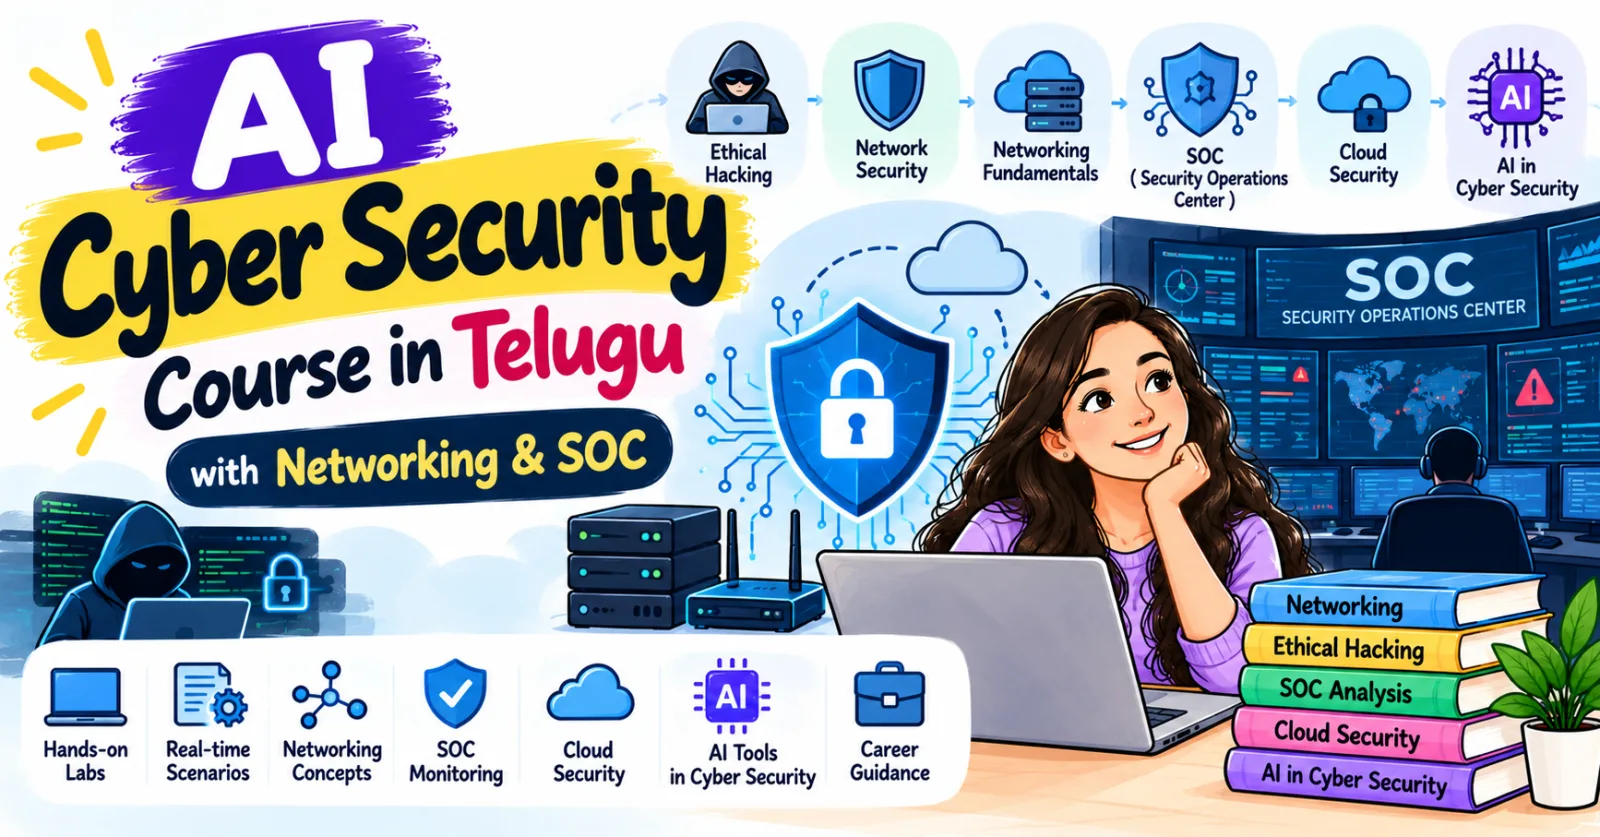
Network security and Security Operations Center (SOC) operations are important areas of cybersecurity. Organizations depend on secure networks to protect business applications, customer information, employee accounts, and digital infrastructure.An AI Cyber Security Course in Telugu with Networking & SOC can help learners explore networking fundamentals, security monitoring, threat detection, and the role of artificial intelligence in modern security operations.
What Is Network Security?
Network security refers to the technologies, policies, and practices used to protect computer networks from unauthorized access, misuse, and cyber threats. It helps organizations control who can access their systems, monitor network activity, and reduce the risk of security incidents.
For example, a company may use firewalls to control incoming and outgoing network traffic. Access controls can restrict sensitive systems to authorized employees, while monitoring tools help identify unusual communication patterns.
Network security involves several areas, including network segmentation, secure communication, access management, intrusion detection, and vulnerability management. Understanding these concepts is essential before moving on to advanced security topics.
Essential Networking Fundamentals
Before learning security tools, beginners should understand how devices communicate across networks.
IP Addresses and Subnetting
An Internet Protocol (IP) address identifies a device or network interface for communication. Subnetting divides a network into smaller logical networks, helping organizations manage addresses and control traffic.
Learn the difference between public and private IP addresses, IPv4 and IPv6, and basic subnet calculations. These concepts are useful when reviewing network configurations and investigating connectivity issues.
DNS and DHCP
The Domain Name System (DNS) translates domain names into IP addresses. Dynamic Host Configuration Protocol (DHCP) helps devices obtain network configuration information automatically.
Understanding these services can help security professionals investigate suspicious domain lookups, unexpected configuration changes, and network-related problems.
TCP, UDP, and Common Ports
TCP and UDP are transport-layer protocols that support different communication requirements. TCP provides reliable, ordered delivery, while UDP offers a connectionless approach with lower protocol overhead.
Beginners should also understand common services such as HTTPS, DNS, SSH, and email protocols. Learning their purposes makes it easier to interpret network traffic and investigate unusual connections.
Firewalls and Network Segmentation
Firewalls apply rules to control network traffic. Network segmentation separates systems into logical areas to limit unnecessary communication and help contain security incidents.
For example, an organization may separate employee devices from sensitive application servers. This approach can reduce the impact of compromised devices when combined with suitable access controls.
Common Network Security Threats
Understanding threats helps security professionals recognize suspicious activity and choose appropriate defensive measures.
Unauthorized access: Occurs when someone accesses a system or resource without permission.
Phishing: Uses deceptive messages to trick people into revealing credentials or opening unsafe links.
Denial-of-service attacks: Attempt to make systems or services unavailable by overwhelming their resources or exploiting weaknesses.
Malware: Refers to software designed to perform harmful or unauthorized activities.
Man-in-the-middle attacks: Involve intercepting or manipulating communication between parties.
Misconfigured services: Expose systems to unnecessary risks when security settings are weak or incorrect.
Organizations address these threats through layered defenses, secure configurations, monitoring, regular updates, employee awareness, and incident response procedures.
What Is a Security Operations Center (SOC)?
A Security Operations Center is a team or function responsible for monitoring an organization's technology environment and investigating potential security incidents.
SOC teams collect information from endpoints, servers, network devices, applications, and security platforms. They examine alerts, investigate suspicious behavior, document findings, and escalate incidents when necessary.
SOC operations commonly involve three activities:
Monitoring: Reviewing alerts and security events.
Investigation: Examining evidence to determine whether an event is suspicious.
Response and escalation: Following approved procedures to contain or resolve incidents.
SOC structures vary between organizations. Some teams provide continuous monitoring, while others use different staffing arrangements or outsource selected security functions.
Important SOC Tools and Technologies
Security Information and Event Management (SIEM)
SIEM platforms collect and analyse logs from different systems. They help security teams correlate events and identify patterns that may indicate threats.
A SIEM alert might identify repeated authentication failures, unusual account activity, or communication with a suspicious destination. Analysts must examine the surrounding evidence before deciding whether the alert represents a genuine incident.
Intrusion Detection and Prevention Systems
Intrusion Detection Systems (IDS) identify potentially suspicious network or system activity. Intrusion Prevention Systems (IPS) can take configured actions to block certain detected activity.
These systems support security monitoring, but their effectiveness depends on configuration, detection rules, and ongoing maintenance.
Conclusion
Mastering network security and SOC fundamentals requires a clear understanding of networking, security controls, threat detection, log analysis, and incident investigation. Beginners should progress from core concepts to practical exercises and gradually explore SIEM, endpoint security, and AI-assisted analysis.
Consistent practice and careful documentation can help learners develop the skills needed to investigate security events and understand organizational defense strategies. By building a strong technical foundation and learning to make evidence-based decisions, aspiring professionals can prepare for further learning and cybersecurity career opportunities.
0 comments
Log in to leave a comment.
Be the first to comment.