
Liquid Cooling Comes to the Secure Data Hall: The Hydronic Boundary Question
Liquid cooling is moving from specialty to mainstream in high-density computing, and the shift has a consequence that thermal engineers and security officers are only beginning to discuss with each other. In an ordinary data hall, replacing air with liquid changes ducts, plant capacity, and floor layout.
In a hall with a classified enclave inside it, the change lands somewhere else as well: on the secure boundary, where the cooling architecture can create new fluid crossings that must be designed, documented, and carried through accreditation.
What Liquid Cooling Changes About the Room
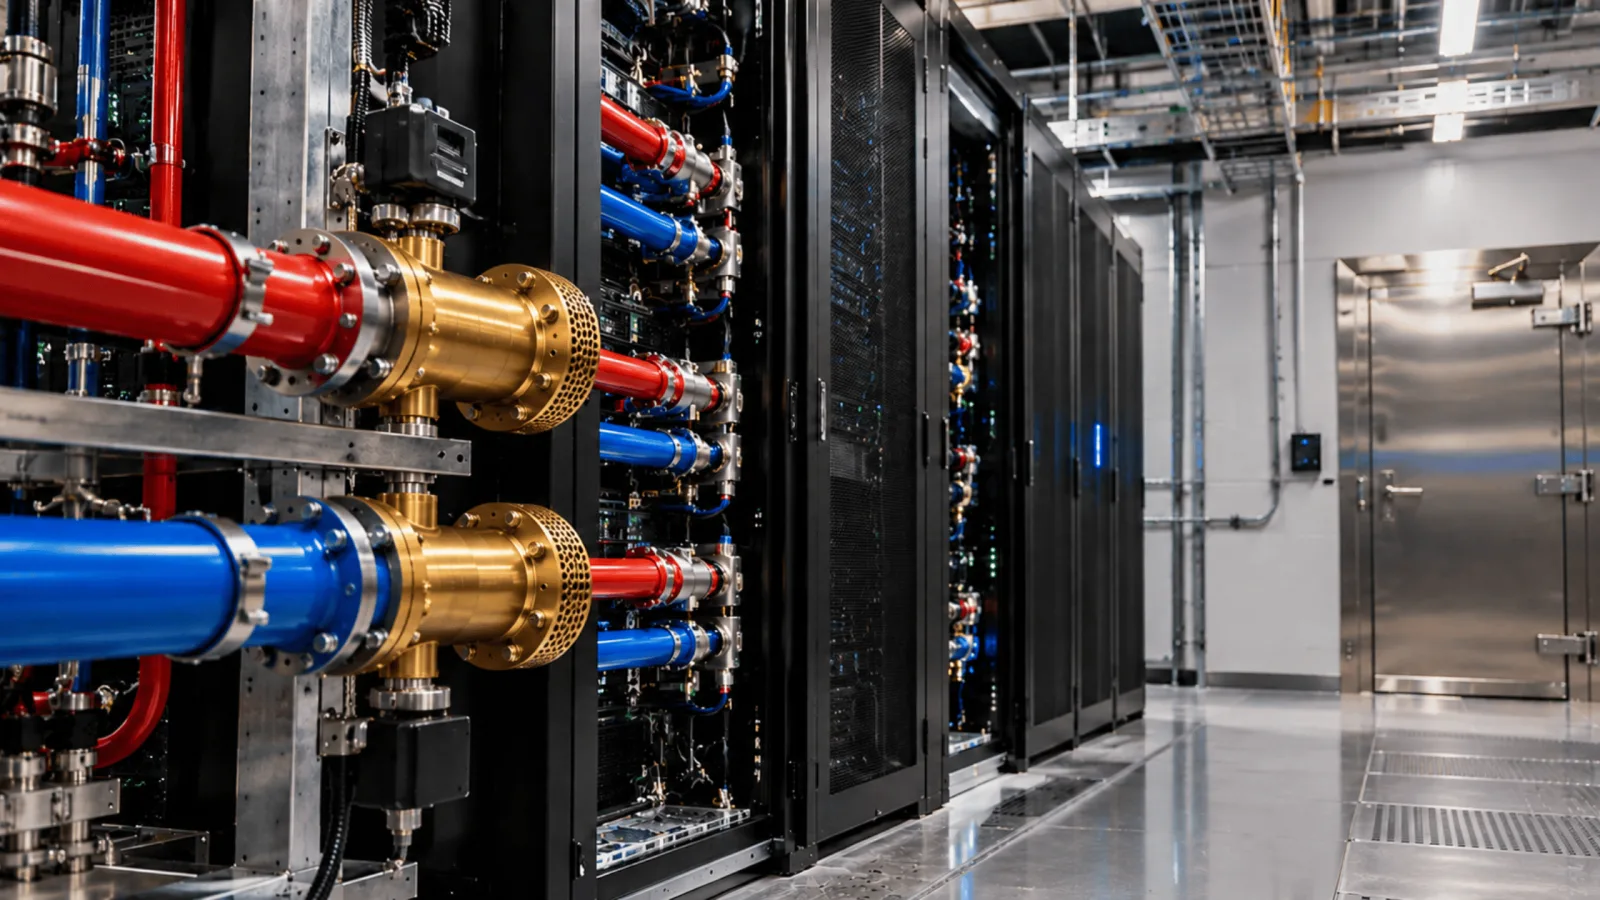
In a conventional air-cooled data hall, much of the heat is transferred from the racks into room air before being removed by the cooling system. Direct liquid cooling shifts more of that heat transfer into piping that reaches much closer to the IT equipment. Cold plates on processors capture much of the heat at the chip, coolant carries it through a technology cooling loop to a coolant distribution unit, and the CDU transfers that heat to the facility-side cooling system.
Industry reporting through 2026 describes rack densities in dense AI clusters running far beyond what air alone can remove, which is why new high-density builds increasingly assume liquid from the start.
The practical result is more pipe, closer to the compute. Supply and return lines now run to the racks themselves, coolant distribution units sit on or near the floor, and liquid distribution extends deeper into the compute space and closer to the racks than in many conventional air-cooled designs. For most facilities, this is a plumbing and commissioning story. For a secure facility, it is a boundary story.
Liquid Cooling Changes the Penetration Count
A classified enclave inside a data hall has a defined perimeter, and ICD 705 and its Technical Specifications treat penetrations of that perimeter as part of the security design.
A metallic coolant line that crosses the boundary is a conductor running from the protected space into the rest of the building, and the opening it passes through has to be coordinated with whatever acoustic and shielding requirements apply to the enclosure.
Where the facility’s security review calls for treatment, the crossing has to preserve the enclosure’s performance while carrying the cooling the computing depends on. The engineering behind fluid penetrations in shielded enclosures covers how that is done; the planning question for enclave teams is how many of those crossings the design creates in the first place.
That number is now a design variable rather than a constant. An air-cooled enclave might have had a handful of mechanical penetrations. A liquid-cooled enclave can create many more internal supply and return lines, and depending on where CDUs, headers, and facility connections are located, some of those design choices can increase the number of boundary crossings. The count depends on decisions the thermal design makes early, often without the security requirements in the room.
The CDU Question Decides the Count
The single most consequential choice is where the coolant distribution units sit relative to the secure boundary. In a liquid-to-liquid architecture, placing CDUs outside the enclave may require the technology cooling supply and return lines to cross the secure boundary. Locating the CDUs inside can instead keep rack-level distribution within the protected space, leaving a smaller number of facility-side cooling connections to cross.
The exact result depends on the CDU architecture, redundancy strategy, and routing. Neither answer is automatically right. Floor space inside an enclave is expensive, service access has security implications, and the thermal design has its own constraints. But the two layouts can produce very different penetration schedules for the same computing load, and the time to compare them is before either is drawn.
Routing discipline does the rest. Lines that merely pass near the enclave should not cross it, headers can be placed so that loops serving unclassified racks never touch the boundary, and every crossing that remains belongs on the penetration schedule with a designed treatment and an owner.
Questions for Enclave Teams Planning Liquid Cooling
- 1. Where do the coolant distribution units sit relative to the secure boundary, and what does each candidate location do to the number of crossings?
- 2. Which crossings are facility-side cooling connections and which are technology cooling loops, and is each matched to the fluid, pressure, temperature, and materials it will actually see?
- 3. Are all SCIF piping penetrations on a single schedule that both the mechanical designer and the security authority have reviewed, with the treatment for each documented for accreditation?
- 4. If the computing load grows and more liquid loops are added later, does the boundary design leave room for new crossings, or will expansion mean reopening a verified enclosure?
The Takeaway
Liquid cooling does not create a new category of secure-boundary problem, but it can increase the number and complexity of fluid services that must be coordinated. Teams that treat penetration count as a design variable, influenced by CDU placement, header location, redundancy, and routing, have a better chance of resolving those crossings before construction and accreditation.
0 comments
Log in to leave a comment.
Be the first to comment.