
Is SoftPOS App Really Secure for Merchants?
Is SoftPOS App secure for merchants? Explore encryption, tokenization, device checks, PCI MPoC standards, and the security precautions behind BrandPos.
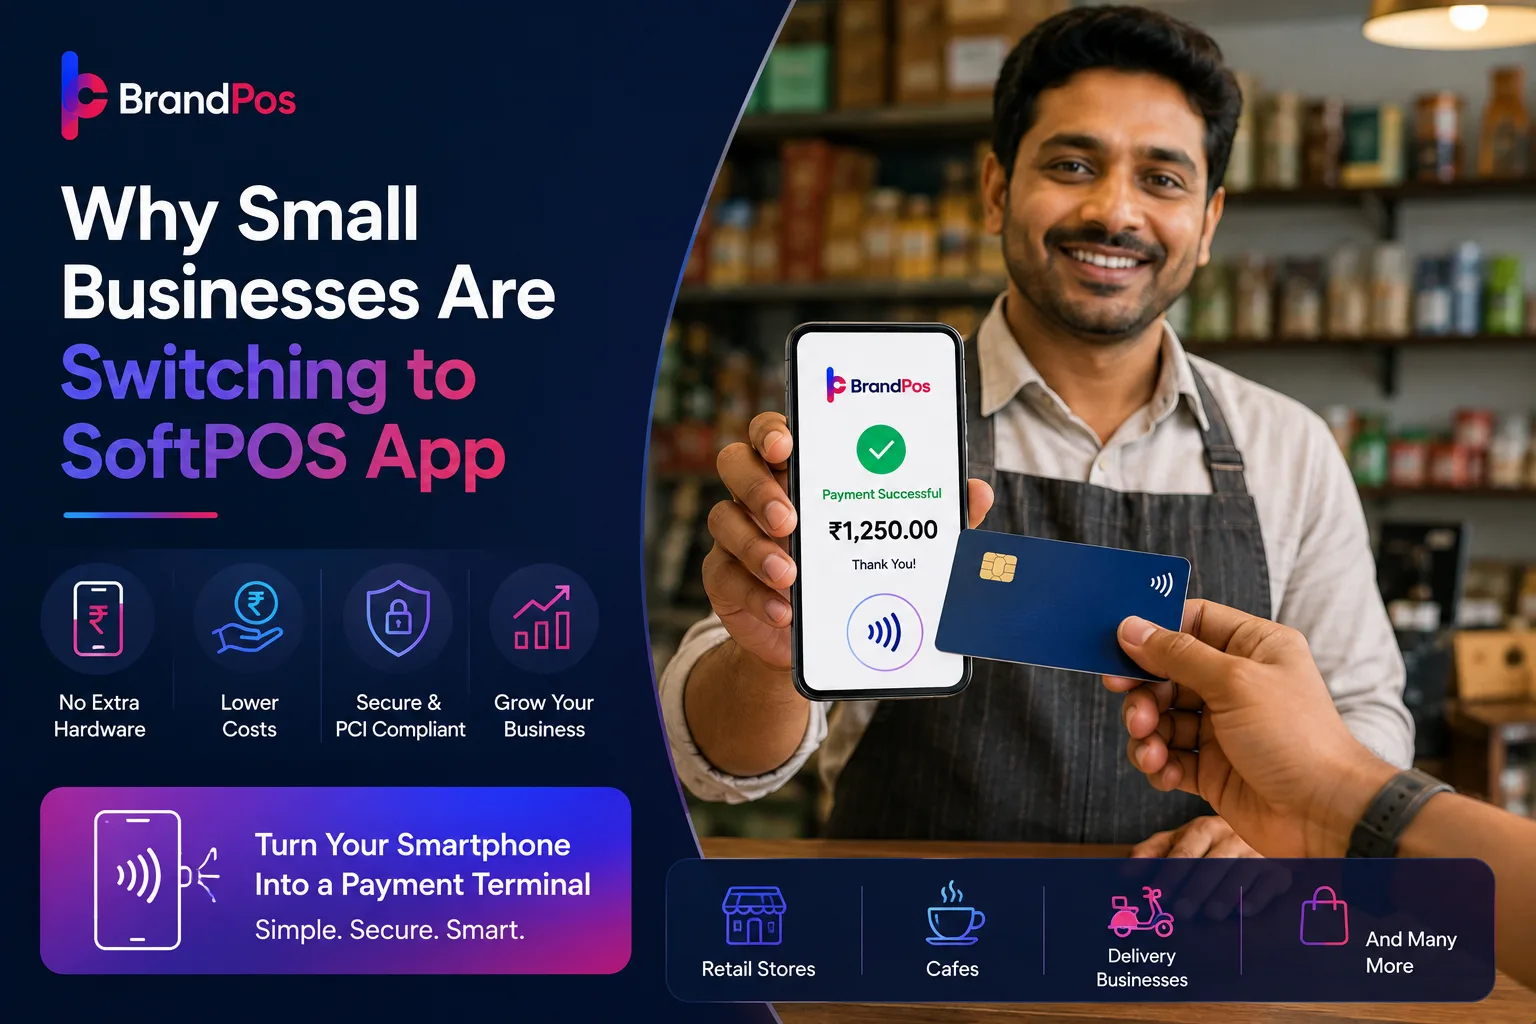
Yes, a SoftPOS app can provide a secure way to accept contactless payments when it uses appropriate payment-security controls, protects transaction data, and operates only on supported devices. BrandPos publicly highlights encrypted transactions, tokenization, and restrictions on rooted or modified Android phones. Merchants should also verify the solution’s current PCI certification and payment-provider requirements before activation.
Why Do Merchants Question SoftPOS Security?
A traditional card terminal looks like dedicated payment equipment. It has a separate keypad, card-reading components, and a physical design associated with payment processing. A SoftPOS solution works differently: it uses a compatible smartphone to accept supported contactless payments.
That difference naturally raises questions.
What happens to card information after a customer taps? Can another app access payment data? What if the phone has been modified? Does the payment app meet recognized industry security standards?
These are reasonable concerns, particularly for restaurants, retailers, hotels, and businesses handling frequent customer transactions.
A properly designed SoftPOS App should not depend on a single security feature. It needs multiple safeguards covering the device, payment application, transaction communication, and processing environment.
What Does PCI MPoC Compliance Mean for Merchants?
PCI MPoC stands for Mobile Payments on Commercial off-the-Shelf devices. It is a security standard developed by the PCI Security Standards Council for payment solutions that accept payments using everyday smartphones and similar devices.
The standard brings together security requirements associated with contactless payment acceptance and PIN entry on commercial mobile devices.
For merchants, an MPoC evaluation is relevant because it addresses how a mobile payment solution protects sensitive information while operating on hardware that was not originally designed exclusively for payment acceptance.
It covers areas such as:
Protection of payment data during processing
Security of payment applications and their components
Device and application integrity
Secure PIN handling where supported
Ongoing monitoring and maintenance of the payment solution
However, PCI DSS, PCI CPoC, and PCI MPoC are not interchangeable labels. A general statement about PCI compliance does not automatically prove that a particular SoftPOS product holds a current MPoC certification.
BrandPos describes its transactions as encrypted and its payment solution as PCI-compliant. Merchants specifically requiring PCI MPoC approval should request the current certificate, solution name, approval scope, and validity details from the provider before treating that certification as confirmed.
The PCI MPoC standard is explained by the PCI Security Standards Council.
How Encryption and Tokenization Protect Payment Data
Encryption helps protect information as it moves between participating payment systems. Instead of transmitting readable payment information, the system uses cryptographic methods to make the data unintelligible to unauthorized parties.
BrandPos publicly identifies secure, encrypted transactions as one of its payment features. This is an important protection because transaction information should not be exposed in readable form during communication between the payment application and its processing environment.
Tokenization provides another layer of protection. It replaces sensitive payment information with a substitute value, known as a token, which is used within the authorized payment environment.
For merchants, this can reduce the need to handle or expose actual payment credentials during routine business operations.
BrandPos also identifies tokenization as part of its payment-processing architecture. However, merchants should request the provider's technical documentation to confirm exactly which card-data elements are tokenized, where they are processed, and whether any sensitive information is temporarily retained.
It would be inaccurate to promise that no card-related data ever touches a device without verified technical documentation. The important distinction is that sensitive payment credentials should be protected by the solution's approved security architecture rather than exposed to ordinary merchant applications.
Why BrandPos Blocks Rooted Android Phones
A smartphone can become less trustworthy when its operating system is rooted or modified.
Root access can remove normal restrictions that prevent applications from accessing protected system resources. Custom ROMs and unauthorized modifications can also change how the operating system handles permissions, security updates, and application behavior.
That creates potential risks for payment applications.
BrandPos identifies rooted phones and custom ROMs as unsupported for its SoftPOS payment flow. This restriction helps maintain a controlled device environment and reduces exposure to unauthorized software changes.
Device integrity checks are another important part of mobile payment security. Depending on the implementation, checks can help identify whether a device is rooted, tampered with, running an unsupported operating system, or otherwise unsuitable for payment acceptance.
For merchants, the practical takeaway is simple: use a supported Android smartphone, install the genuine application through an authorized store, and keep the operating system updated. A phone that works normally for calls and messaging may still fail the security requirements for contactless payment acceptance.
What Security Layers Protect Every SoftPOS Transaction?
Several safeguards work together to protect the payment process:
Transaction encryption: Helps protect payment information while it travels through authorized communication channels.
Tokenization: Replaces sensitive payment credentials with tokens within the supported processing environment.
Device integrity controls: Help identify rooted, modified, or unsupported smartphones.
Application security: Helps prevent unauthorized software changes and access to protected payment functions.
Payment processing controls: Route transactions through the authorized payment infrastructure and applicable security checks.
Merchant account protection: Onboarding and identity-verification procedures help establish legitimate merchant access.
These controls reduce common security risks, but no payment technology can guarantee that every fraudulent attempt will be prevented.
What Must Merchants Check Before Using SoftPOS App?
Before adopting a SoftPOS App for Android, merchants should check more than the app's advertised features.
Certification: Ask whether the exact solution holds PCI MPoC, PCI CPoC, or another applicable approval. Request documentary evidence.
Device compatibility: Confirm that the Android phone has NFC and meets the provider's operating-system and security requirements.
Root detection: Check whether rooted devices, custom ROMs, and unsupported modifications are blocked.
Data handling: Ask how card information is encrypted, tokenized, processed, and retained.
Payment authorization: Confirm the internet and connectivity requirements for transaction authorization.
Updates and support: Understand how security updates are delivered and how unsupported devices are handled.
One limitation deserves particular attention: SoftPOS generally needs an internet connection to communicate with the payment-processing infrastructure and obtain authorization. A customer may be standing directly in front of the merchant, but the payment cannot necessarily be completed if the phone has lost connectivity. Offline payment support should never be assumed.
SoftPOS App vs Card Reader: Security
Neither option is automatically more secure in every situation. Security depends on the specific solution, certification scope, payment provider, device controls, and how the merchant manages the equipment.
A German Restaurant Owner's Security Concern: An Illustrative Scenario
Imagine a restaurant owner in Germany who wants to replace several traditional card terminals with smartphone-based payment acceptance.
The owner likes the convenience of accepting contactless payments at the counter and directly at customer tables. However, the main concern is not convenience. It is whether customer card information will remain protected.
Before switching, the owner asks BrandPos for details about encryption, tokenization, device restrictions, and PCI certification.
The provider's published information helps explain its encrypted transaction approach, tokenization, and restrictions on rooted or modified Android devices. The owner also requests documentary evidence of the precise PCI certification held by the payment solution.
That final step matters. If PCI MPoC certification is a business requirement, the owner should switch only after receiving and validating the relevant certificate and confirming that it covers the deployed solution.
This is a sensible security-first purchasing decision: evaluate the actual safeguards, verify the certification, and then test the payment workflow before moving the entire restaurant to a new system.
Final Thoughts
A smartphone-based payment solution should be judged by its security architecture, not simply by the fact that it runs on a phone.
BrandPos publicly highlights encrypted transactions, tokenization, and restrictions on rooted or modified Android devices. These are meaningful elements of a layered payment-security approach. Merchants should still verify the exact PCI certification, data-handling arrangements, and device requirements that apply to their account and payment setup.
For businesses considering a SoftPOS App, the right approach is to ask clear questions, review the supporting documentation, and test the solution on compatible devices before deployment. Security should be established through verifiable controls, not marketing language.
Frequently Asked Questions
1. Can a Customer’s Card Details Be Stolen When They Tap on a SoftPOS Phone?
A properly secured payment solution uses safeguards such as encryption and tokenization to reduce exposure of sensitive payment information. Merchants should check the provider's technical documentation for its exact data-handling process.
2. Does PCI MPoC Certification Apply to Every Android Phone?
No. MPoC evaluates a payment solution and its security controls, not every smartphone universally. The phone must also meet the solution's compatibility and device-integrity requirements.
3. Why Can't Merchants Use Rooted Phones for Contactless Payments?
Rooting can weaken normal operating-system protections and allow unauthorized access to system resources. Blocking rooted or modified devices helps maintain a more controlled payment environment.
4. Can a SoftPOS Transaction Go Through Without Mobile Data or Wi-Fi?
Usually, the phone needs an internet connection to communicate with the payment processor and receive authorization. Merchants should confirm whether their provider supports any specific offline functionality rather than assuming it is available.
5. What Certification Should a Merchant Ask for Before Choosing a SoftPOS Provider?
Ask for the exact PCI MPoC or PCI CPoC certification applicable to the product, along with its solution name, approval scope, and validity. A general PCI compliance statement is not proof of a specific MPoC certification.
0 comments
Log in to leave a comment.
Be the first to comment.