
How Key Management Helps Organizations Improve Control Over Cryptographic Keys
Organizations increasingly rely on cryptographic keys to protect data, authenticate systems, secure applications, and support digital services. Effective Key management helps businesses improve visibility, access control, rotation, recovery, and lifecycle governance for these key

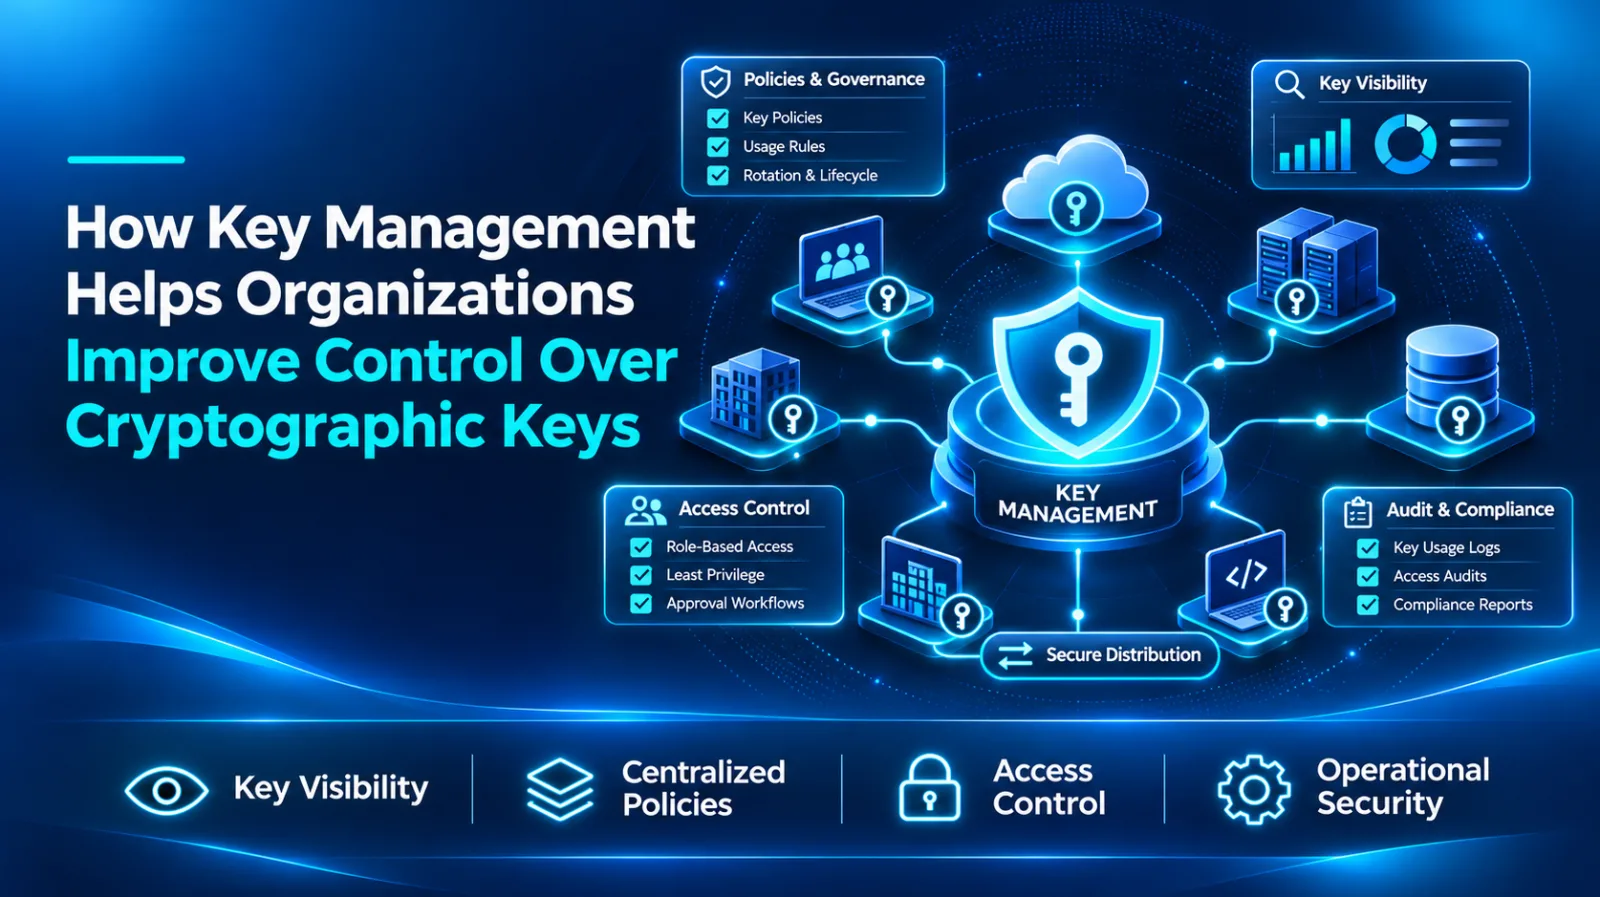
Introduction
Cryptography plays an important role in modern cybersecurity.
Organizations use cryptographic technologies to encrypt sensitive information, authenticate users and applications, secure communications, create digital signatures, and protect digital certificates.
All these functions can depend on cryptographic keys.
As organizations expand their IT environments, they may create large numbers of keys across databases, applications, cloud platforms, APIs, backup systems, and other infrastructure.
Managing these keys manually or through disconnected systems can make it difficult to maintain visibility and control.
This is why effective Key management has become an important enterprise security requirement.
A structured approach to key management in cryptography helps organizations manage cryptographic keys throughout their lifecycle and establish stronger controls over access, usage, rotation, recovery, and retirement.
What Is Key Management?
Key management refers to the policies, processes, and technologies organizations use to control cryptographic keys.
It is not limited to storing keys securely.
A complete Key management strategy addresses:
Key generation
Key storage
Key distribution
Key access
Key usage
Key rotation
Key backup
Key recovery
Key retirement
Key destruction
Each stage requires appropriate controls.
Why Organizations Lose Control of Cryptographic Keys
Key management becomes difficult when organizations grow quickly.
Different teams may create keys independently for:
Applications
Databases
Cloud storage
APIs
Backup systems
Digital certificates
Over time, security teams may lose track of which keys exist and what they protect.
This situation creates key sprawl.
Building a Centralized Key Inventory
The first step toward stronger control involves visibility.
Organizations should maintain a reliable inventory of cryptographic keys.
The inventory should include:
Key identifier
Key owner
Purpose
Associated system
Protected information
Access permissions
Rotation schedule
Lifecycle status
An accurate inventory allows security teams to make better decisions.
Key Management in Cryptography
Key management in cryptography provides the lifecycle framework organizations use to control cryptographic assets.
A practical lifecycle can follow:
Generate → Store → Access → Use → Rotate → Recover → Retire → Destroy
Organizations should establish policies for each stage.
Improving Access Control
Access control represents one of the most important aspects of Key management.
Organizations should follow least privilege.
Users and applications should receive only the permissions required for their business functions.
For example, an application that encrypts customer information should not automatically have access to keys used by an unrelated internal application.
Managing Key Ownership
Every important key should have a defined owner.
Ownership should include responsibility for:
Purpose
Access
Rotation
Recovery
Retirement
Clear ownership improves accountability.
It also helps security teams respond quickly when a key requires immediate action.
Key Rotation
Organizations should rotate cryptographic keys according to defined policies.
Rotation can help reduce unnecessary exposure associated with long-lived keys.
Rotation requirements may depend on:
Key age
Data sensitivity
Risk
Security policies
Application requirements
Suspected compromise
Organizations should test rotation before applying it to critical systems.
Key Recovery
Organizations must also prepare for key loss or unavailability.
If a critical encryption key becomes unavailable, authorized users may lose access to protected information.
Businesses should maintain secure backups and documented recovery procedures.
Recovery access should receive strict controls.
Protecting Keys From Application Exposure
Developers sometimes store keys in application source code or configuration files.
This can create unnecessary exposure.
Organizations should provide applications with controlled access to cryptographic services.
This approach reduces the number of places where sensitive keys exist.
Managing Keys Across Cloud Environments
Cloud platforms can introduce additional Key management challenges.
Organizations may operate across multiple cloud providers.
Each cloud environment may host applications, databases, storage systems, and other workloads.
Security teams should maintain visibility across these environments.
A centralized approach can help organizations establish common Key management policies.
Managing Hybrid Infrastructure
Hybrid infrastructure combines cloud and on-premises systems.
A business may operate:
Cloud applications
On-premises databases
Cloud backup
Private infrastructure
Cryptographic keys may support all these systems.
Organizations should maintain consistent policies across environments while accounting for technical differences.
Monitoring Key Activity
Organizations should monitor cryptographic activity.
Important events include:
Key creation
Key access
Key rotation
Administrative changes
Failed access attempts
Key retirement
Monitoring can help security teams detect unusual behavior.
Retiring Obsolete Keys
Organizations should review keys when systems or applications become obsolete.
Unused keys should not remain active indefinitely.
Security teams should establish procedures for key retirement and destruction.
This reduces unnecessary cryptographic exposure.
Protecting Digital Certificates
Digital certificates rely on cryptographic keys.
Organizations should track certificate-related assets throughout their lifecycle.
They should monitor:
Certificate ownership
Expiration
Renewal
Private key protection
Retirement
This helps reduce certificate-related security and availability risks.
Key Management and Database Security
Databases often contain sensitive business information.
Organizations use encryption to protect database records.
The encryption keys should remain protected separately from the database.
Effective Key management helps control access to these keys and maintain lifecycle policies.
Supporting Incident Response
Organizations should integrate Key management with incident response.
If a cryptographic key becomes compromised, security teams need to know:
Which key was affected
What systems use it
What information it protects
Who can access it
How to replace it
A documented process can reduce response time.
Common Key Management Challenges
Key Sprawl
Organizations may accumulate large numbers of keys.
Poor Visibility
Security teams may not know where all keys reside.
Excessive Permissions
Applications may receive unnecessary access.
Manual Processes
Manual rotation can create errors.
Unclear Ownership
Teams may not know who manages specific keys.
Best Practices for Better Key Control
Organizations should:
Maintain a complete cryptographic inventory.
Assign clear ownership.
Apply least privilege.
Separate keys from protected data.
Establish rotation policies.
Protect key backups.
Monitor key activity.
Automate suitable lifecycle processes.
Test recovery procedures.
Retire obsolete keys.
Review access permissions regularly.
Integrate Key management with incident response.
Conclusion
Cryptographic keys protect many of the systems and services that businesses depend on.
However, organizations can lose control of these assets when keys become fragmented across applications, databases, cloud platforms, and infrastructure.
Key management in cryptography provides the lifecycle framework needed to control these keys.
Effective Key management improves visibility, ownership, access control, rotation, recovery, monitoring, and retirement.
By establishing centralized policies and maintaining an accurate cryptographic inventory, organizations can reduce key sprawl and strengthen control over the cryptographic infrastructure supporting their enterprise security strategy.
0 comments
Log in to leave a comment.
Be the first to comment.