
How Key Management Helps Enterprises Control Encryption Keys Across Multiple Applications
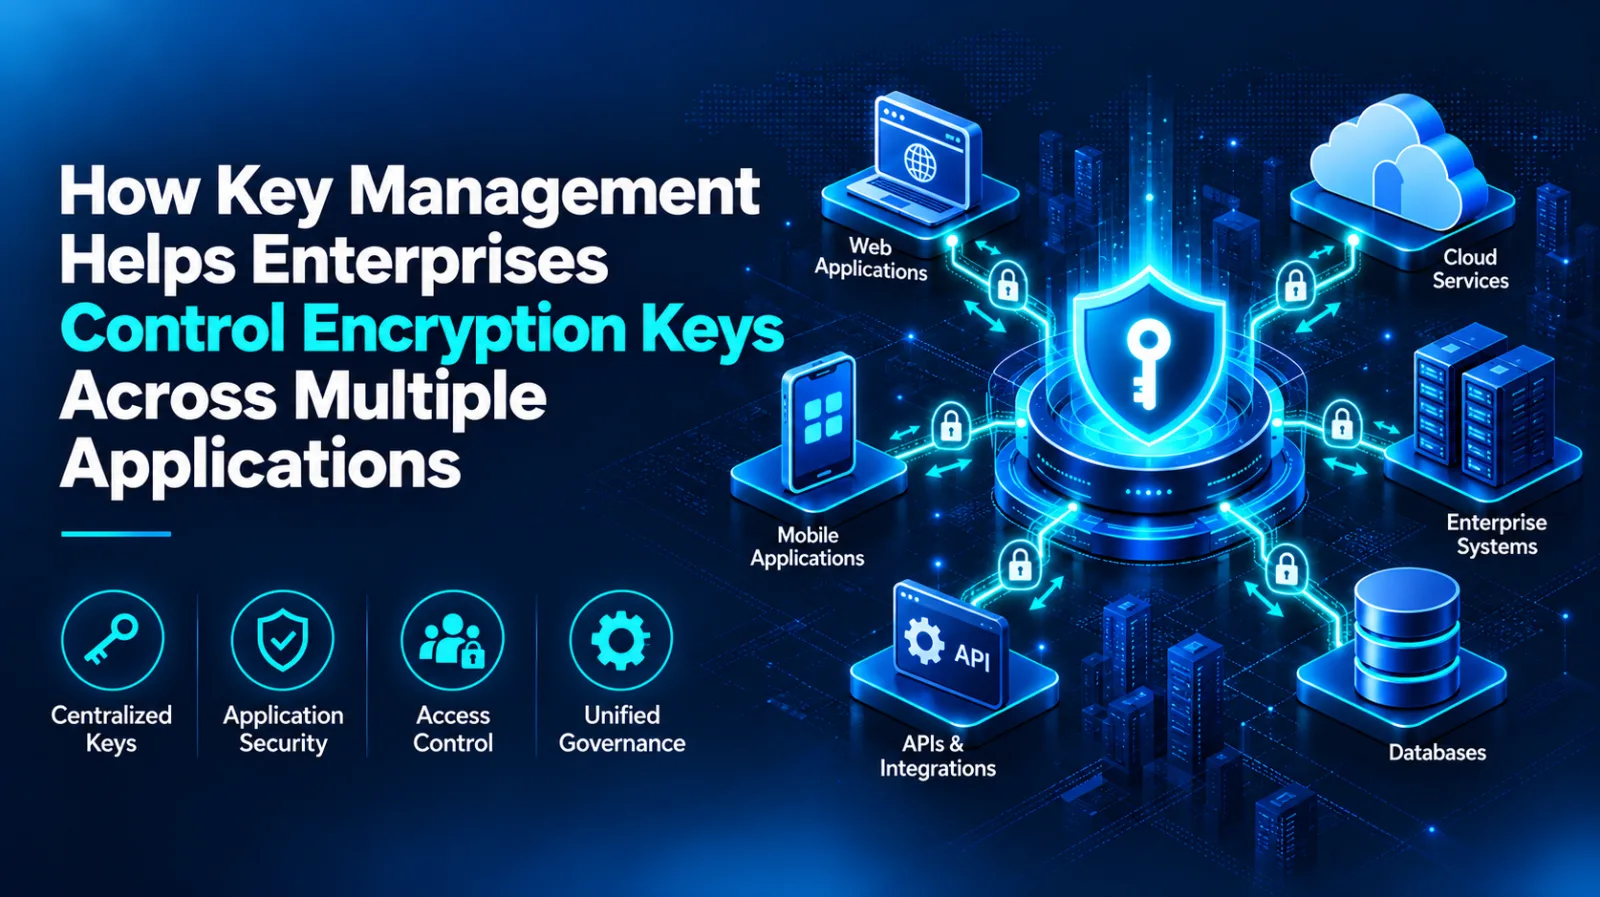
Enterprises often use hundreds of applications that depend on encryption keys to protect sensitive data and secure digital operations. Key management helps organizations maintain control over these keys by establishing consistent access, lifecycle, rotation, and monitoring polici

Introduction
Modern enterprises rely on a large number of applications to support daily operations.
Organizations may use customer portals, ERP platforms, CRM systems, financial applications, HR systems, analytics tools, mobile applications, APIs, and cloud services.
Many of these applications process sensitive information.
Encryption helps protect this information, but encryption keys create another security responsibility.
If every application manages its own keys independently, organizations can quickly lose visibility and control.
This can lead to key sprawl, inconsistent policies, excessive access permissions, and difficult lifecycle management.
Effective Key management provides a structured way for enterprises to control cryptographic keys across multiple applications.
Why Applications Need Cryptographic Keys
Applications may use cryptographic keys for several purposes.
These include:
Data encryption
API authentication
Digital signatures
Secure communication
Database encryption
Certificate-based authentication
Each key should have a defined purpose and lifecycle.
Organizations should avoid treating cryptographic keys as ordinary configuration values.
Understanding Key Management
Key management includes the policies, processes, and technologies used to manage cryptographic keys.
The lifecycle generally includes:
Generation
Storage
Access
Usage
Rotation
Backup
Recovery
Retirement
Destruction
A structured lifecycle helps organizations maintain better control.
The Role of Key Management in Cryptography
Key management in cryptography provides the framework for protecting keys throughout their lifecycle.
Organizations should determine:
Who owns each key
Which application uses it
What information it protects
Who can access it
When it should rotate
When it should retire
This information creates accountability.
The Problem of Application-Level Key Management
Application teams may create keys independently.
One team may store keys in configuration files, another may use a cloud service, and another may maintain keys within an application environment.
This fragmentation creates challenges.
Security teams may struggle to determine:
How many keys exist
Which keys remain active
Who owns them
Which applications depend on them
Centralized Key management can reduce these problems.
Creating a Key Inventory
Organizations should maintain an accurate inventory.
A useful inventory can include:
An accurate inventory improves visibility.
Applying Least Privilege
Applications should receive only the cryptographic permissions they need.
For example, a payroll application should not automatically have access to keys used by a customer-facing application.
Least privilege limits unnecessary exposure.
Security teams should review permissions regularly.
Avoiding Hard-Coded Keys
Hard-coded keys can create serious security risks.
Developers may accidentally expose keys through:
Source code repositories
Application packages
Configuration files
Deployment scripts
Organizations should provide secure mechanisms for applications to access cryptographic services.
Managing Keys Across Development Environments
Applications often move through several environments:
Development
Testing
Staging
Production
Organizations should avoid using production keys in development environments unless there is a specific and controlled requirement.
Separate keys can reduce the impact of a compromised development environment.
Key Rotation Across Applications
Key rotation becomes more complicated when several applications depend on the same key.
Before rotation, security teams should identify dependencies.
They should determine:
Which applications use the key
Which databases depend on it
Which services need updates
Whether older keys must remain available temporarily
A planned process reduces service interruptions.
Managing Cloud Applications
Cloud applications may use encryption for:
Databases
Storage
Backups
Application data
APIs
Organizations should include these keys within their enterprise Key management framework.
This creates greater consistency between cloud and on-premises applications.
Managing Database Keys
Enterprise applications often depend on databases.
Database encryption can protect sensitive records, but the corresponding keys require separate protection.
Security teams should know which applications depend on each database encryption key.
This improves lifecycle management.
Managing API Keys and Cryptographic Credentials
Applications may use cryptographic credentials to communicate through APIs.
Organizations should track these credentials and establish:
Ownership
Access controls
Rotation
Expiration
Revocation
Credentials should not remain active after an application or integration is retired.
Monitoring Key Usage
Organizations should monitor cryptographic activity across applications.
Important events include:
Key access
Key creation
Key rotation
Failed access attempts
Administrative changes
Key retirement
Monitoring can help security teams identify unusual activity.
Key Backup and Recovery
Critical applications may depend on encryption keys.
If an organization loses a key, authorized users may lose access to protected information.
Businesses should maintain secure backups and test recovery procedures.
Retiring Application Keys
When an application reaches the end of its lifecycle, organizations should review its associated cryptographic keys.
Unused keys should not remain active indefinitely.
Security teams should determine whether keys need to be retained for historical data access or can be securely retired.
Common Challenges
Key Sprawl
Large application portfolios can generate many cryptographic keys.
Inconsistent Practices
Different teams may follow different procedures.
Excessive Permissions
Applications may receive unnecessary access.
Poor Documentation
Teams may not know which applications depend on specific keys.
Legacy Applications
Older applications may not support modern Key management mechanisms.
Best Practices
Organizations should:
Maintain a centralized key inventory
Assign key ownership
Apply least privilege
Separate keys by environment where appropriate
Avoid hard-coded keys
Establish rotation policies
Monitor key access
Protect backups
Test recovery
Review application dependencies
Retire obsolete keys
Integrate Key management with application security
Building a Centralized Application Key Strategy
A practical approach can follow:
Discover → Inventory → Classify → Assign ownership → Protect → Monitor → Rotate → Retire
This lifecycle helps organizations maintain control as the application environment grows.
Conclusion
Enterprise applications depend increasingly on cryptography to protect sensitive information and secure digital communication.
Managing the associated keys independently within every application can create unnecessary complexity.
Key management in cryptography provides the framework for managing keys throughout their lifecycle.
Effective Key management improves visibility, access control, rotation, backup, recovery, monitoring, and retirement.
By centralizing key governance and integrating cryptographic controls into application security practices, enterprises can reduce key sprawl and maintain stronger control over the encryption keys protecting their business applications.
0 comments
Log in to leave a comment.
Be the first to comment.