
How a DPO Dashboard Simplifies GDPR and EU AI Act Compliance
Empower your DPO with AnnexOps Command Center. Get centralized visibility of AI systems, risk classification, compliance status, and audit readiness for EU AI Act compliance.
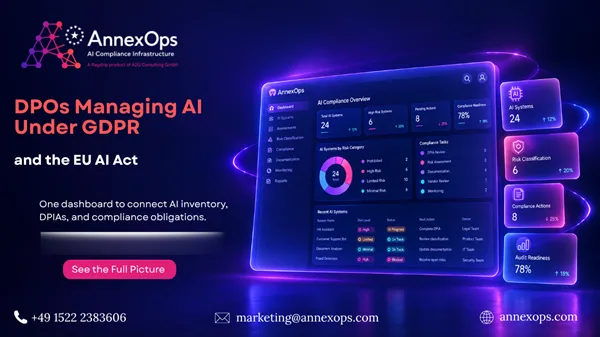
Data protection teams are no longer managing privacy compliance in isolation. As organizations adopt AI for customer service, hiring, analytics, content generation, risk assessment, and other business processes, Data Protection Officers (DPOs) increasingly need visibility into both GDPR requirements and AI governance activities.
This is where a DPO Dashboard can become useful.
Instead of managing AI inventories, privacy assessments, compliance tasks, documentation, and evidence across disconnected spreadsheets and documents, organizations can use a centralized dashboard to bring these activities together.
Why DPOs Need Better Visibility Into AI Systems
One of the biggest challenges for DPOs is knowing exactly where AI is being used across an organization.
An organization may have AI tools operated by different departments, third-party AI services integrated into existing products, or machine-learning features embedded into business processes. Without a structured inventory, it can be difficult to understand which systems process personal data, what their purpose is, or which regulatory obligations may apply.
A centralized AI inventory gives DPOs a starting point for understanding the organization's AI landscape.
From there, privacy and compliance teams can examine questions such as:
What personal data does an AI system process?
What is the purpose of the processing?
Which legal or regulatory requirements apply?
Is a Data Protection Impact Assessment (DPIA) required?
What role does the organization have in relation to the AI system?
What documentation and evidence should be maintained?
Which compliance activities still need attention?
A DPO dashboard can make this information easier to organize and monitor.
Connecting GDPR and EU AI Act Workflows
GDPR and the EU AI Act address different regulatory areas, but they can overlap when AI systems process personal data.
For example, an organization deploying an AI system may need to consider data protection principles while also assessing whether the system falls within the scope of specific EU AI Act requirements.
This creates a practical challenge for DPOs and privacy teams: compliance information needs to be connected rather than managed as completely separate processes.
An effective DPO compliance dashboard can help provide a centralized view of relevant activities, including:
AI system inventories
Data protection assessments
AI risk classification
Processing activities
Documentation
Compliance tasks
Evidence management
Human oversight requirements
AI governance activities
The goal is not simply to create another reporting interface. The dashboard should help teams understand what needs to be reviewed, documented, updated, or followed up.
What Should a DPO Dashboard Include?
The exact features will depend on an organization's size and AI governance structure. However, several capabilities can make a DPO dashboard particularly useful.
1. AI System Inventory
The first step is visibility.
A centralized inventory can provide information about the AI systems being developed, purchased, or deployed across an organization. This can include details about the system's purpose, owner, provider, use case, data processing activities, and regulatory status.
This information gives DPOs a clearer starting point for privacy and AI governance reviews.
2. Risk and Classification Tracking
AI systems can have different regulatory implications depending on their intended purpose and use.
An AI risk assessment can help organizations determine which systems require additional review and which regulatory obligations may be relevant.
For EU AI Act compliance, organizations may need to consider factors such as whether an AI system falls under prohibited practices, high-risk categories, transparency requirements, or other applicable provisions.
A dashboard can make these assessments easier to track over time.
3. DPIA Management
A Data Protection Impact Assessment can be an important part of GDPR compliance when processing is likely to result in a high risk to individuals.
For organizations using AI with personal data, DPIAs may need to be considered alongside AI governance activities.
A centralized dashboard can help teams track DPIA status, responsible stakeholders, identified risks, mitigation measures, approvals, and supporting documentation.
This reduces the need to search through separate files whenever an assessment needs to be reviewed.
4. Compliance Task Management
Compliance is an ongoing process rather than a one-time exercise.
A DPO may need to monitor incomplete assessments, missing documentation, policy reviews, evidence collection, vendor information, and other governance activities.
A dashboard can provide a consolidated view of these tasks and help teams identify outstanding work.
This becomes particularly useful as the number of AI systems grows.
5. Documentation and Evidence
Regulatory compliance often requires organizations to maintain records demonstrating how requirements have been addressed.
Keeping evidence in multiple locations can make audits and internal reviews unnecessarily difficult.
A centralized compliance workspace can help associate documents and evidence with the relevant AI system, assessment, obligation, or compliance activity.
This creates a clearer audit trail for internal stakeholders and compliance teams.
Moving From Spreadsheets to Continuous Compliance Management
Spreadsheets can be useful when an organization has only a small number of AI systems. However, they can become difficult to maintain as AI adoption increases.
Information can become outdated. Different departments may maintain separate versions. Important compliance actions can be missed. Changes to an AI system may not be reflected consistently across documentation.
A DPO Dashboard can provide a more structured approach.
Instead of viewing compliance as a collection of individual documents, teams can manage it as an ongoing workflow:
Discover → Assess → Classify → Document → Review → Monitor
This approach gives DPOs and AI governance teams a clearer picture of the organization's current compliance position.
How AnnexOps Approaches the DPO Dashboard
For organizations looking to connect GDPR and EU AI Act governance activities, AnnexOps DPO Dashboard provides a centralized environment for managing AI compliance operations.
The dashboard is designed to help teams maintain visibility into AI systems, risk classification, compliance activities, documentation, and evidence.
Rather than treating AI governance and privacy work as disconnected processes, AnnexOps brings relevant information into a centralized workflow.
You can explore the AnnexOps DPO Dashboard to see how it can support GDPR and EU AI Act compliance operations.
What DPOs Should Look for in a Compliance Dashboard
Choosing a dashboard should depend on the organization's actual compliance workflow rather than the number of features listed by a vendor.
DPOs and privacy teams can consider whether the solution provides:
Centralized visibility: Can the team see relevant AI systems and their compliance status in one place?
AI governance capabilities: Can the dashboard support AI inventory, risk assessment, classification, and governance activities?
GDPR integration: Can privacy assessments and data protection activities be connected to AI systems?
Evidence management: Can supporting documentation be associated with relevant compliance activities?
Task tracking: Can teams identify outstanding actions and responsible owners?
Ongoing monitoring: Can information be reviewed and updated as AI systems and regulatory requirements change?
These considerations are particularly important for organizations managing multiple AI systems across different departments.
The Role of DPOs in AI Governance
The role of the DPO is becoming increasingly connected to AI governance where AI systems involve personal data or create data protection implications.
DPOs may need to collaborate with legal, security, engineering, product, procurement, and compliance teams to understand how AI is being developed and used.
A centralized dashboard does not replace this collaboration. Instead, it can provide a shared source of information that makes those discussions easier.
When everyone works from the same AI inventory and compliance records, organizations can reduce information gaps and make follow-up activities more structured.
Final Thoughts
As AI becomes part of everyday business operations, DPOs need more than isolated privacy documentation. They need visibility into where AI is being used, what data is involved, which risks have been identified, and what compliance activities remain open.
A DPO Dashboard can bring these workflows together and provide a more organized way to manage GDPR and EU AI Act requirements.
For organizations building a structured AI governance process, centralizing AI inventories, assessments, documentation, evidence, and compliance tasks can make ongoing oversight easier to manage.
The objective is not to treat compliance as a static checklist. It is to build a process that can evolve as AI systems, business operations, and regulatory requirements change.
Contact us: +49 1522 2383606Email at: [email protected]
0 comments
Log in to leave a comment.
Be the first to comment.