
Enterprise AI Governance in Malaysia: Security, PDPA and AI Risk Management Explained
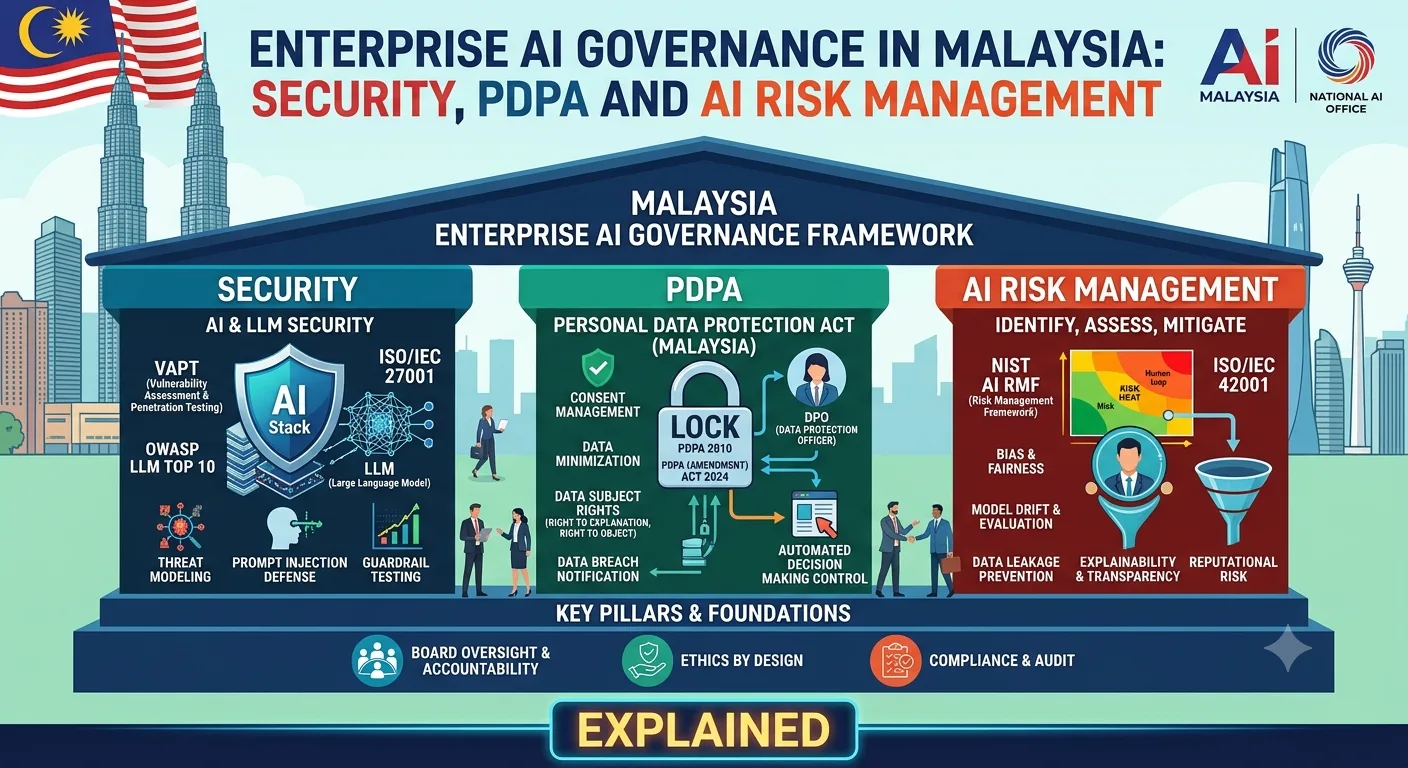
Artificial intelligence is transforming how enterprises operate, analyse data, automate workflows, and serve customers. From intelligent chatbots and predictive analytics to AI-powered decision-making, Malaysian businesses are increasingly exploring AI to improve productivity and competitiveness. However, adopting AI at scale also introduces challenges involving data privacy, cybersecurity, regulatory compliance, transparency, and operational risk.
For enterprise leaders, AI adoption is no longer just a technology decision. It requires a structured governance framework that establishes accountability, protects sensitive information, and ensures AI systems operate reliably. Malaysia's National Guidelines on AI Governance and Ethics (AIGE) provide voluntary guidance for responsible AI development and use, while existing legislation, including the Personal Data Protection Act 2010 (PDPA), remains relevant to applicable business activities.
Understanding these requirements helps enterprises build AI systems that support innovation without overlooking security and compliance. Working with an experienced AI Software Development Company in Malaysia can also help businesses integrate governance into their AI development lifecycle.
What Is Enterprise AI Governance and Why Does It Matter?
Enterprise AI governance refers to the policies, processes, technical controls, and accountability structures that guide how an organisation develops, deploys, and manages artificial intelligence. It ensures that AI initiatives align with business objectives, security requirements, ethical principles, and applicable regulations.
Without proper governance, enterprises may face inaccurate AI-generated outputs, biased decisions, unauthorised data access, unclear accountability, and unexpected operational costs.
A practical AI governance framework typically includes:
Accountability: Assigning clear ownership for AI systems, decisions, and incidents.
Data governance: Managing data quality, access, retention, and appropriate usage.
Security controls: Protecting models, applications, APIs, and connected data sources.
Risk assessment: Evaluating potential harm before deploying AI systems.
Human oversight: Establishing review and escalation procedures for sensitive decisions.
Continuous monitoring: Tracking system performance, accuracy, security, and compliance.
These measures help enterprises establish consistent standards across departments rather than allowing individual teams to implement AI without appropriate oversight.
Understanding Malaysia's AI Governance Framework
Malaysia is developing its AI ecosystem through national policies, guidelines, and initiatives that encourage responsible innovation. The National Guidelines on AI Governance and Ethics (AIGE), introduced in September 2024, outline seven principles: fairness, reliability, safety and control, privacy and security, inclusiveness, transparency, accountability, and the pursuit of human benefit and happiness.
These principles provide a foundation for organisations seeking to implement responsible AI practices.
Although AIGE is voluntary guidance rather than a standalone binding AI law, enterprises should consider its principles when establishing internal governance policies. Existing legal obligations may still apply depending on the organisation, industry, data, and use case. Malaysia's AI governance landscape continues to evolve, making regular policy reviews important.
For example, a financial services organisation using AI to evaluate customer applications should assess potential bias, document its decision-making process, protect personal information, and establish human review procedures. Similarly, a manufacturer deploying predictive maintenance should evaluate data security, model reliability, and the consequences of inaccurate predictions.
An effective governance strategy translates high-level principles into practical controls, documented responsibilities, and measurable operational standards.
How Malaysia's PDPA Applies to Enterprise AI Systems
The Personal Data Protection Act 2010 (PDPA) regulates the processing of personal data in applicable commercial transactions in Malaysia. Organisations using AI to process customer, employee, supplier, or other personal information must assess their obligations under the Act and applicable amendments.
AI applications can introduce additional privacy considerations because they may collect, combine, analyse, or generate information about individuals.
1. Establish a Lawful Basis for Data Processing
Before using personal data to train, fine-tune, or operate an AI model, businesses should evaluate the purpose of processing and the applicable legal requirements. They should communicate relevant information to individuals and obtain consent where required.
Using customer information for an unrelated AI training purpose without assessing its permissibility can create privacy and compliance risks.
2. Minimise Personal Data Exposure
Enterprises should collect and process only the information necessary for the intended AI use case. Data masking, pseudonymisation, anonymisation where appropriate, and restricted access can reduce unnecessary exposure.
For example, an internal support chatbot may not need full customer identifiers to answer routine questions. Removing or masking unnecessary information can reduce the impact of potential data leaks.
3. Review Data Retention and Individual Rights
Businesses should establish retention schedules, deletion procedures, and processes for handling applicable data access and correction requests. They should also consider how personal information is stored in AI logs, vector databases, training datasets, and third-party platforms.
4. Assess Cross-Border Data Transfers
Cloud-based AI platforms may process or store information outside Malaysia. Organisations should assess applicable PDPA requirements for cross-border transfers, vendor arrangements, security safeguards, and data locations before selecting a deployment model.
Malaysia's PDPA amendments also introduced changes involving areas such as data breach notification, data protection officers, and data processor security obligations. Businesses should review the provisions and implementation requirements applicable to their operations.
Enterprise AI Security Risks Businesses Must Address
AI systems create security challenges beyond those associated with conventional software applications. A secure implementation must consider the entire technology stack, including data pipelines, models, APIs, infrastructure, and external integrations.
Key risks include:
Data leakage: Sensitive business information may be exposed through poorly configured AI tools, prompts, logs, or third-party services.
Prompt injection: Malicious instructions embedded in user inputs or retrieved documents may manipulate an AI application into bypassing intended safeguards.
Unauthorised access: Excessive permissions can allow users or AI agents to retrieve confidential documents, execute restricted actions, or access systems beyond their responsibilities.
Model manipulation: Compromised training data, malicious inputs, or manipulated retrieval sources can affect model reliability and output quality.
Third-party vulnerabilities: External model providers, plugins, APIs, and cloud services can introduce dependencies that require security assessment.
To reduce these risks, enterprises should implement encryption, identity and access management, least-privilege permissions, secure API authentication, input validation, output filtering, and regular security testing. AI agents that can perform actions should have narrowly defined permissions and require approval for sensitive transactions.
Security controls should be tested before deployment and reviewed whenever models, datasets, integrations, or business requirements change.
Building an Effective AI Risk Management Framework
AI risk management should begin before development and continue throughout the system's operational lifecycle. A risk-based approach helps enterprises allocate stronger controls to applications with greater potential for harm.
A practical framework includes five steps.
Step 1: Identify and Classify AI Use Cases
Create an inventory of AI applications and document their purposes, users, data sources, dependencies, and business impact. Classify each use case according to its potential consequences, sensitivity, and level of autonomy.
Step 2: Conduct Risk and Impact Assessments
Evaluate privacy, cybersecurity, bias, reliability, legal obligations, and operational risks. Consider what could happen if the system produces an incorrect recommendation, exposes information, or takes an unauthorised action.
Step 3: Implement Appropriate Controls
Map identified risks to technical and organisational safeguards. High-impact applications may require stronger testing, restricted permissions, human approval, documented validation, and additional monitoring.
Step 4: Maintain Human Oversight and Accountability
Assign an owner to every production AI system. Define who can approve deployment, investigate incidents, override automated decisions, and suspend a system when risks become unacceptable.
Step 5: Monitor and Improve Continuously
Track model accuracy, output quality, unusual access patterns, security incidents, and changes in data or system behaviour. Periodically reassess risks and maintain documentation of important updates and decisions.
This lifecycle approach makes AI governance an ongoing business capability rather than a one-time compliance exercise.
How to Implement AI Governance in Enterprise Software Development
Governance is most effective when built into the software development process from the beginning. Retrofitting security and compliance controls after an AI application goes live can increase remediation costs and create avoidable operational disruption.
Enterprises should define governance requirements during discovery and architecture planning. Development teams can then incorporate data protection, access controls, audit logging, testing, and human review into the solution design.
For retrieval-augmented generation (RAG) systems, for instance, access permissions should be enforced when retrieving enterprise documents. The model should not expose confidential information simply because it exists in the connected knowledge base.
Similarly, AI-powered workflow automation should include action limits, approval checkpoints, error handling, and traceable execution logs.
Choosing an AI Software Development Company in Malaysia with an understanding of enterprise architecture, secure engineering, and responsible AI practices can help businesses translate these requirements into scalable applications.
How Hidden Brains Supports Enterprise AI Initiatives
Hidden Brains helps businesses explore AI-driven digital transformation through AI development and software engineering capabilities. Enterprises can evaluate their business processes, identify suitable automation opportunities, and plan AI implementations around their operational requirements.
With a structured development approach, businesses can consider security, data governance, system integration, scalability, and ongoing monitoring as part of their AI strategy.
The goal is to develop AI applications that address genuine business challenges while accounting for relevant privacy, security, and governance requirements. Organisations should also establish appropriate internal ownership and obtain legal or regulatory guidance when their use cases involve complex compliance obligations.
Businesses evaluating AI adoption can exploreAI Software Development Company in Malaysia to learn more about Hidden Brains' AI development capabilities.
Conclusion
Enterprise AI governance in Malaysia requires a balance between innovation, security, accountability, and privacy. By considering the PDPA, applying responsible AI principles, assessing risks, and embedding security controls throughout the development lifecycle, organisations can build a stronger foundation for AI adoption.
Effective governance also requires continuous monitoring, clear ownership, documented procedures, and regular reviews as technology and regulatory expectations evolve. With the right strategy and implementation partner, enterprises can adopt AI more confidently while protecting business data, maintaining customer trust, and supporting long-term growth.
0 comments
Log in to leave a comment.
Be the first to comment.