
DPDP Consent Managers in India: What Businesses Need to Know Before November 2026
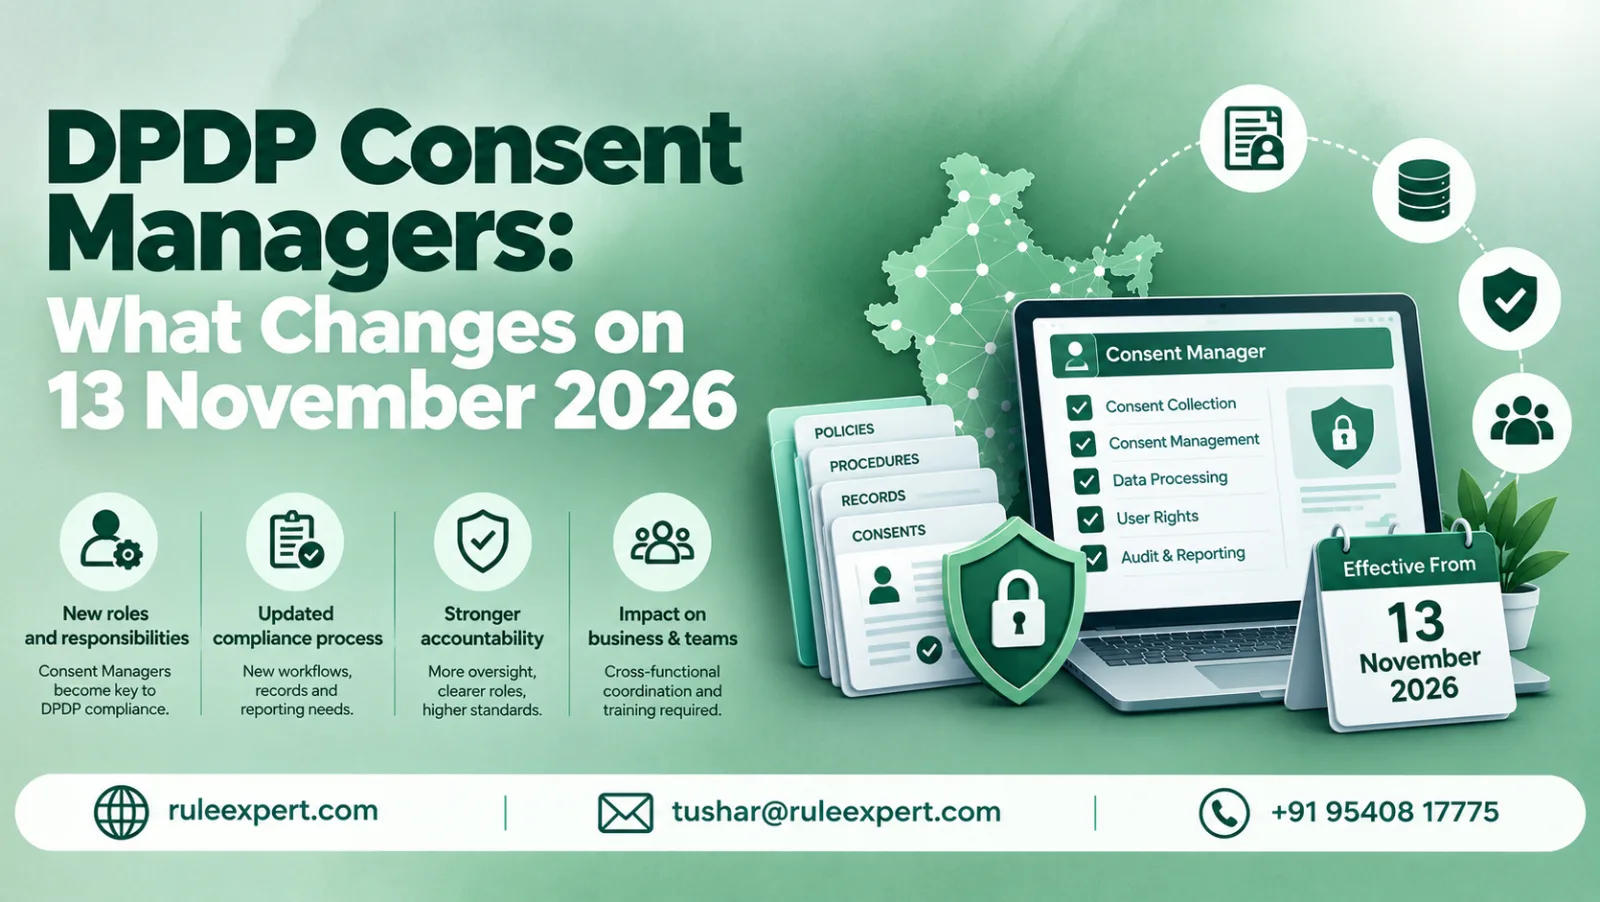
India's data protection landscape is entering an important phase with the implementation of the Digital Personal Data Protection (DPDP) Act, 2023, and the DPDP Rules, 2025. One of the significant developments under this framework is the introduction of registered Consent Managers, which will give individuals greater control over how their personal data is shared and how their consent is managed.
From November 13, 2026, eligible companies can apply to the Data Protection Board of India for registration as Consent Managers under Section 6(9) of the DPDP Act and Rule 4 of the DPDP Rules.
Although this development does not mean that every business must immediately register with or integrate a Consent Manager, it introduces an important operational consideration for organizations that collect and process personal data.
Businesses should begin understanding how consent instructions may reach their systems and how those instructions can be implemented across internal applications, vendors, and third-party service providers.
What Is a Consent Manager Under the DPDP Act?
A Consent Manager is a registered entity that provides individuals, known as Data Principals under the DPDP Act, with a centralized platform to give, manage, review, and withdraw their consent.
Instead of interacting separately with multiple businesses, individuals can use a Consent Manager as a single point of contact for managing consent across different Data Fiduciaries.
For example, an individual may have shared personal information with a banking application, an e-commerce platform, and a financial services provider. Through a registered Consent Manager, the individual can manage relevant consent decisions in a more organized manner.
Under the Act, a Consent Manager acts in a fiduciary capacity toward the individual. Its responsibility is to facilitate the individual's consent choices rather than represent the interests of the businesses processing the data.
What Happens on November 13, 2026?
November 13, 2026, is an important milestone because Section 6(9) of the DPDP Act and Rule 4 of the DPDP Rules become applicable.
This opens the registration process for eligible companies that want to operate as Consent Managers.
However, it is important to distinguish this date from the wider compliance timeline.
The registration provisions for Consent Managers begin on November 13, 2026, while the principal obligations concerning notices, consent, security safeguards, personal data breaches, and Data Principal rights are scheduled to take effect for Data Fiduciaries on May 13, 2027.
This phased implementation gives businesses additional time to prepare their systems and processes.
For organizations, the immediate priority should be understanding the upcoming framework and preparing for the possibility of receiving consent-related instructions through registered intermediaries.
Who Can Become a Registered Consent Manager?
Not every software company or consent management service provider automatically qualifies as a Consent Manager under the DPDP framework.
The registration requirements include specific eligibility conditions.
Some of the important requirements include:
- The applicant must be a company incorporated in India.
- It must maintain a minimum net worth of ₹2 crore.
- Its directors must satisfy the prescribed integrity requirements.
- Its platform must undergo independent certification.
- It must meet the governance, operational, and technical conditions prescribed under the DPDP Rules.
The Data Protection Board will assess applications in accordance with the applicable registration framework.
Businesses should therefore distinguish between a registered Consent Manager and an ordinary consent management software provider.
A consent management platform may help an organization maintain consent records, display notices, and process withdrawal requests. However, this does not automatically make the software provider a registered Consent Manager under the DPDP Act.
How Will Consent Managers Change Business Operations?
The introduction of Consent Managers may influence how organizations receive and implement consent-related decisions.
Consider a financial services company that collects customer information through its mobile application and shares relevant information with an SMS provider, an analytics platform, and other service providers.
A customer may use a registered Consent Manager to withdraw consent for receiving promotional messages.
The business must then ensure that the withdrawal is reflected in its relevant systems and communicated to the appropriate service providers.
Simply recording the withdrawal in the primary application may not be sufficient if other systems continue processing personal data for the same purpose.
This makes coordination between internal teams and external vendors particularly important.
Organizations should establish clear processes to ensure that consent decisions are accurately recorded, communicated, and implemented throughout their data processing ecosystem.
Important Obligations of Registered Consent Managers
The DPDP Rules establish specific requirements for entities operating as registered Consent Managers.
Some important provisions include:
1. Protection of Personal Data
A Consent Manager's platform must be designed so that the entity cannot read the personal data passing through it. Its role is to facilitate consent management rather than access the underlying personal information.
2. Maintenance of Consent Records
Consent Managers must maintain records of consent given, refused, and withdrawn, along with relevant notices and information about sharing with Data Fiduciaries.
The prescribed retention period is at least seven years, unless a longer period is agreed upon or required by law.
3. Independent Governance
Consent Managers must satisfy the prescribed governance and operational requirements. They cannot freely transfer or outsource their core obligations in a manner inconsistent with the Rules.
4. Accountability to Individuals
A registered Consent Manager must operate in the interests of the Data Principal and maintain the transparency and accountability required under the framework.
These requirements are intended to establish trust in the Consent Manager ecosystem.
What Should Businesses Do Before May 2027?
Even though the registration process begins in November 2026, businesses should not wait until the final compliance deadline to improve their consent management processes.
The following activities can help organizations prepare.
1. Identify Consent-Based Processing Activities
Prepare an inventory of all business activities that rely on consent. Identify the personal data involved, the purpose of processing, and the systems where the relevant information is stored.
2. Review Existing Consent Mechanisms
Examine website forms, mobile applications, customer portals, subscription systems, and marketing platforms to determine whether consent is properly collected and recorded.
3. Maintain Reliable Consent Records
Organizations should be able to establish when consent was obtained, which notice was presented, what purpose was communicated, and whether the individual subsequently withdrew consent.
4. Develop a Withdrawal Management Process
Create an internal workflow for receiving, authenticating, recording, and implementing withdrawal requests.
5. Review Vendor and Processor Agreements
Businesses should examine contracts with cloud service providers, marketing agencies, analytics vendors, and other processors to establish how consent-related instructions will be communicated and implemented.
6. Prepare for Technical Integration
Organizations should monitor technical standards and operational guidance published by the Data Protection Board. They should develop flexible internal processes rather than prematurely committing to an integration design before the relevant standards are available.
Common Misunderstandings About DPDP Consent Managers
Several misconceptions could lead organizations to take the wrong approach.
- Every business must become a Consent Manager: Incorrect. Only entities seeking to operate as registered Consent Managers need to apply for registration.
- Businesses must immediately purchase a Consent Manager service: Incorrect. The use of a Consent Manager is an individual's choice under Section 6(7).
- Every consent management software provider is a registered Consent Manager: Incorrect. Registration with the Data Protection Board is a separate legal requirement.
- Consent withdrawal only needs to be recorded in one application: Incorrect. Businesses must consider relevant downstream processing and vendor arrangements.
- November 2026 is the deadline for all DPDP obligations: Incorrect. The broader set of Data Fiduciary obligations is scheduled to take effect on May 13, 2027.
Understanding these distinctions will help businesses avoid unnecessary expenditure and focus on meaningful compliance preparation.
Building a Future-Ready Consent Management Framework
Consent management should not be treated as an isolated legal or technical activity. It requires coordination between legal, compliance, IT, product, marketing, and vendor management teams.
Organizations should aim to establish a structured framework that connects consent collection, recordkeeping, withdrawal handling, data mapping, and third-party processing.
Technology can support this process through centralized consent records, automated workflows, audit trails, and withdrawal management capabilities.
However, software alone cannot guarantee compliance. Organizations must also define responsibilities, review operational procedures, and ensure that their actual data processing activities align with their privacy commitments.
Conclusion
The introduction of registered Consent Managers marks an important development in India's data protection framework. Starting November 13, 2026, eligible entities can apply for registration, creating a new mechanism through which individuals can exercise greater control over their consent decisions.
For businesses, the immediate requirement is not to become a Consent Manager but to prepare their internal systems to recognize and implement valid consent-related instructions.
Organizations that invest early in consent records, withdrawal workflows, vendor governance, and data visibility will be better positioned for the wider DPDP compliance requirements coming into effect in May 2027.
To understand the registration timeline, eligibility criteria, business responsibilities, and practical preparation steps in greater detail, read the complete guide to DPDP Consent Managers and the November 13, 2026 milestone.
Preparing today can help businesses build a more transparent, accountable, and individual-centric approach to personal data protection in India.
0 comments
Log in to leave a comment.
Be the first to comment.