
DPDP Compliance for SaaS Companies: Why a Data Protection Gap Assessment Is Essential
The rapid growth of Software-as-a-Service (SaaS) businesses has transformed how organizations collect, process, store, and manage personal information. From customer onboarding and subscription management to analytics and technical support, SaaS platforms handle significant volumes of personal data every day.
With India's Digital Personal Data Protection (DPDP) Act, 2023, and the DPDP Rules, 2025, introducing a structured framework for personal data protection, SaaS companies need to take a closer look at their privacy and data governance practices.
Having a privacy policy or implementing basic security controls is no longer enough. Businesses must understand how personal data moves across their technology infrastructure, identify compliance weaknesses, and establish processes that support their legal obligations.
This is where a DPDP gap assessment for SaaS companies becomes particularly important.
Understanding DPDP Compliance for SaaS Businesses
SaaS companies often operate across multiple data environments. They collect information from their own customers, process data uploaded by business clients, and share information with external technology providers.
Under the DPDP framework, a company may operate as both a Data Fiduciary and a Data Processor, depending on the nature and purpose of data processing.
For example:
- A SaaS company collecting registration details from its subscribers generally acts as a Data Fiduciary.
- When it processes employee or customer information on behalf of another business, it may act as a Data Processor.
- Cloud hosting providers, analytics platforms, and other technology partners may act as subprocessors.
Understanding these different responsibilities is essential because compliance requirements and contractual obligations can vary depending on the company's role.
What Is a DPDP Gap Assessment?
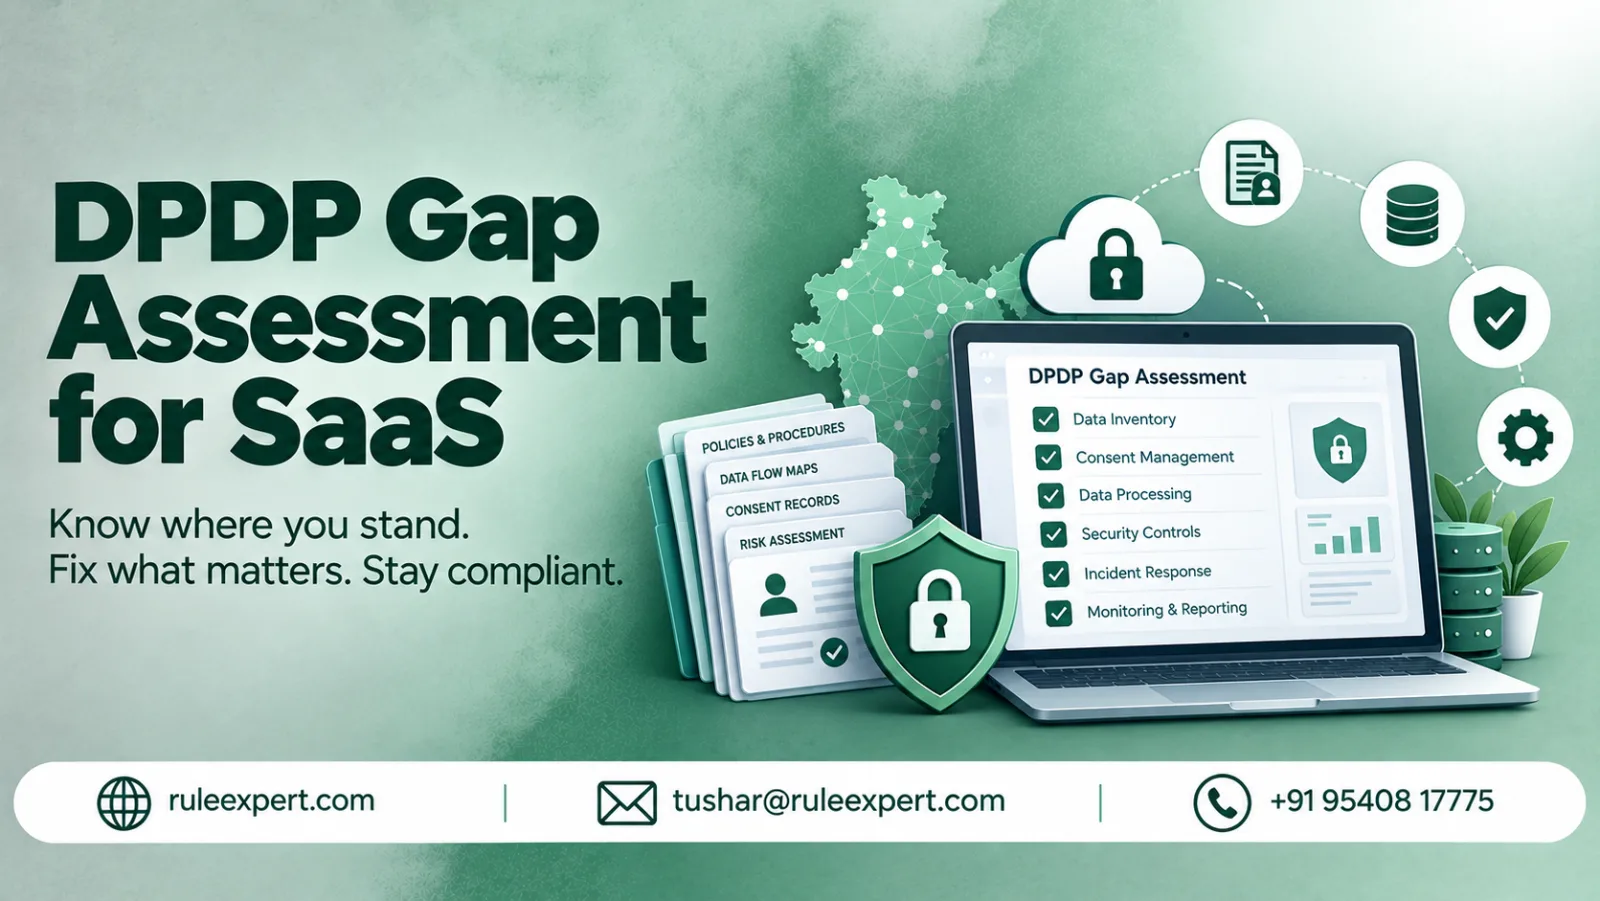
A DPDP gap assessment is a systematic evaluation of an organization's existing data protection practices against applicable requirements under the DPDP Act and Rules.
For SaaS businesses, the assessment examines how personal data is collected, processed, accessed, transferred, retained, and deleted.
It helps organizations identify areas where their current processes may not meet regulatory expectations.
A comprehensive assessment generally evaluates:
- Data collection and consent management: Whether personal data is collected for clearly defined purposes and whether appropriate notices and consent mechanisms are implemented where required.
- Data inventory and mapping: Whether the organization knows what personal information it collects, where it is stored, and which systems or individuals can access it.
- Vendor and subprocessor management: Whether third-party service providers are identified, evaluated, and governed through appropriate contractual arrangements.
- Data retention and deletion: Whether retention schedules are defined and whether personal information is deleted or disposed of according to applicable requirements.
- Data principal rights: Whether processes exist to handle requests relating to access, correction, erasure, and grievance redressal.
- Personal data breach management: Whether the company can identify, investigate, and communicate relevant data breaches within applicable timelines.
Common DPDP Compliance Gaps Found in SaaS Companies
Although SaaS businesses often have mature technical infrastructure, certain privacy-related weaknesses can remain unnoticed.
1. Incomplete Data Mapping
Organizations may know what information their primary application collects but overlook personal data stored in support systems, analytics platforms, development environments, and internal databases.
Without a complete data inventory, identifying the location and movement of personal information becomes difficult.
2. Inadequate Consent and Privacy Notices
A privacy policy may exist, but it may not accurately describe actual data processing activities.
For instance, organizations may use analytics, tracking technologies, or customer engagement tools without properly reflecting those activities in their notices and consent processes.
3. Uncontrolled Access to Customer Information
Technical support teams, administrators, and developers may have access to customer environments.
Without role-based access controls, access reviews, and activity monitoring, unnecessary exposure of personal information can occur.
4. Weak Vendor Governance
SaaS businesses frequently depend on cloud infrastructure providers, payment gateways, communication platforms, and analytics vendors.
An outdated vendor register or missing contractual safeguards can create compliance risks.
Businesses should maintain visibility into their subprocessors and ensure appropriate contractual arrangements are in place.
5. Improper Data Retention Practices
Customer data may remain in backups, application logs, development environments, or support exports even after it has been deleted from the primary application.
This creates a gap between the organization's stated deletion commitments and its actual technical practices.
6. Unclear Data Breach Response Procedures
A company may have general incident management procedures but lack a structured process for identifying affected customers, determining the scope of a breach, and supporting applicable notification obligations.
For SaaS providers serving multiple business customers, tenant-level incident identification is particularly important.
How SaaS Companies Can Conduct an Effective DPDP Gap Assessment
A structured assessment helps organizations move beyond documentation and evaluate how privacy controls work in practice.
The following approach can provide a useful starting point.
Step 1: Identify Personal Data Processing Activities
Document the categories of personal information collected through websites, applications, customer portals, and internal business systems.
Step 2: Map Data Flows
Understand how information moves between production databases, cloud infrastructure, analytics tools, customer support systems, and external vendors.
Step 3: Review Privacy Documentation
Evaluate privacy notices, consent mechanisms, data processing agreements, internal policies, and customer contracts.
Step 4: Evaluate Technical and Organizational Safeguards
Review access permissions, encryption practices, monitoring systems, retention settings, and incident response procedures.
Step 5: Assess Vendor Relationships
Identify third-party service providers and subprocessors, review contractual obligations, and evaluate how personal information is shared with them.
Step 6: Prepare a Risk-Based Remediation Plan
Classify identified gaps according to their potential impact and regulatory relevance. Assign responsibility, establish deadlines, and track corrective actions.
Why DPDP Compliance Is More Than a Documentation Exercise
One of the biggest misconceptions about data protection compliance is that preparing policies and agreements is sufficient.
For SaaS organizations, actual implementation matters just as much as documentation.
Consider a company that promises customers that their information will be deleted within a specified period after contract termination. However, customer records may still exist in backups, support exports, application logs, or testing environments.
The organization must understand these data locations and establish appropriate retention and deletion procedures that account for applicable legal requirements.
Similarly, a vendor agreement may include data protection clauses, but the company should also verify whether the actual vendor relationships, access arrangements, and data-sharing practices reflect those commitments.
A successful DPDP assessment therefore combines legal review, operational evaluation, and technical verification.
Benefits of Conducting a DPDP Gap Assessment Early
Taking a proactive approach to compliance offers several business advantages:
- Reduced regulatory exposure: Identifying weaknesses early helps organizations address potential compliance issues.
- Improved customer confidence: Transparent data handling practices strengthen trust among enterprise customers.
- Better vendor accountability: Structured vendor governance improves visibility into third-party data processing.
- Operational efficiency: Documented data flows and standardized privacy procedures reduce uncertainty.
- Stronger business readiness: Demonstrable compliance practices can support enterprise procurement, security reviews, and customer due diligence.
For growing SaaS companies, these benefits can contribute to long-term business sustainability.
Conclusion
The DPDP Act represents an important development in India's personal data protection landscape. For SaaS companies, meeting its requirements involves more than updating privacy policies or introducing consent banners.
Businesses need visibility into their complete data ecosystem, including customer records, internal systems, development environments, third-party integrations, and subprocessors.
A well-structured DPDP gap assessment helps organizations identify weaknesses, prioritize remediation, and build privacy practices that align with their operational realities.
SaaS businesses looking to understand the assessment process in greater detail can explore this resource on DPDP Gap Assessment for SaaS: Product, Vendor and Customer Data Gaps an Assessor Will Look For.
Taking the time to assess existing practices today can help organizations build a more accountable, transparent, and privacy-conscious SaaS environment.
0 comments
Log in to leave a comment.
Be the first to comment.