
DevSecOps Roadmap for Startups: What to Implement in 30, 60, and 90 Days
Most startups meet security the hard way. A prospect sends a security questionnaire, an investor asks for a compliance timeline, or a leaked API key turns up in a public repository. Fixing things at that point slows releases and costs far more than building security in from the start.
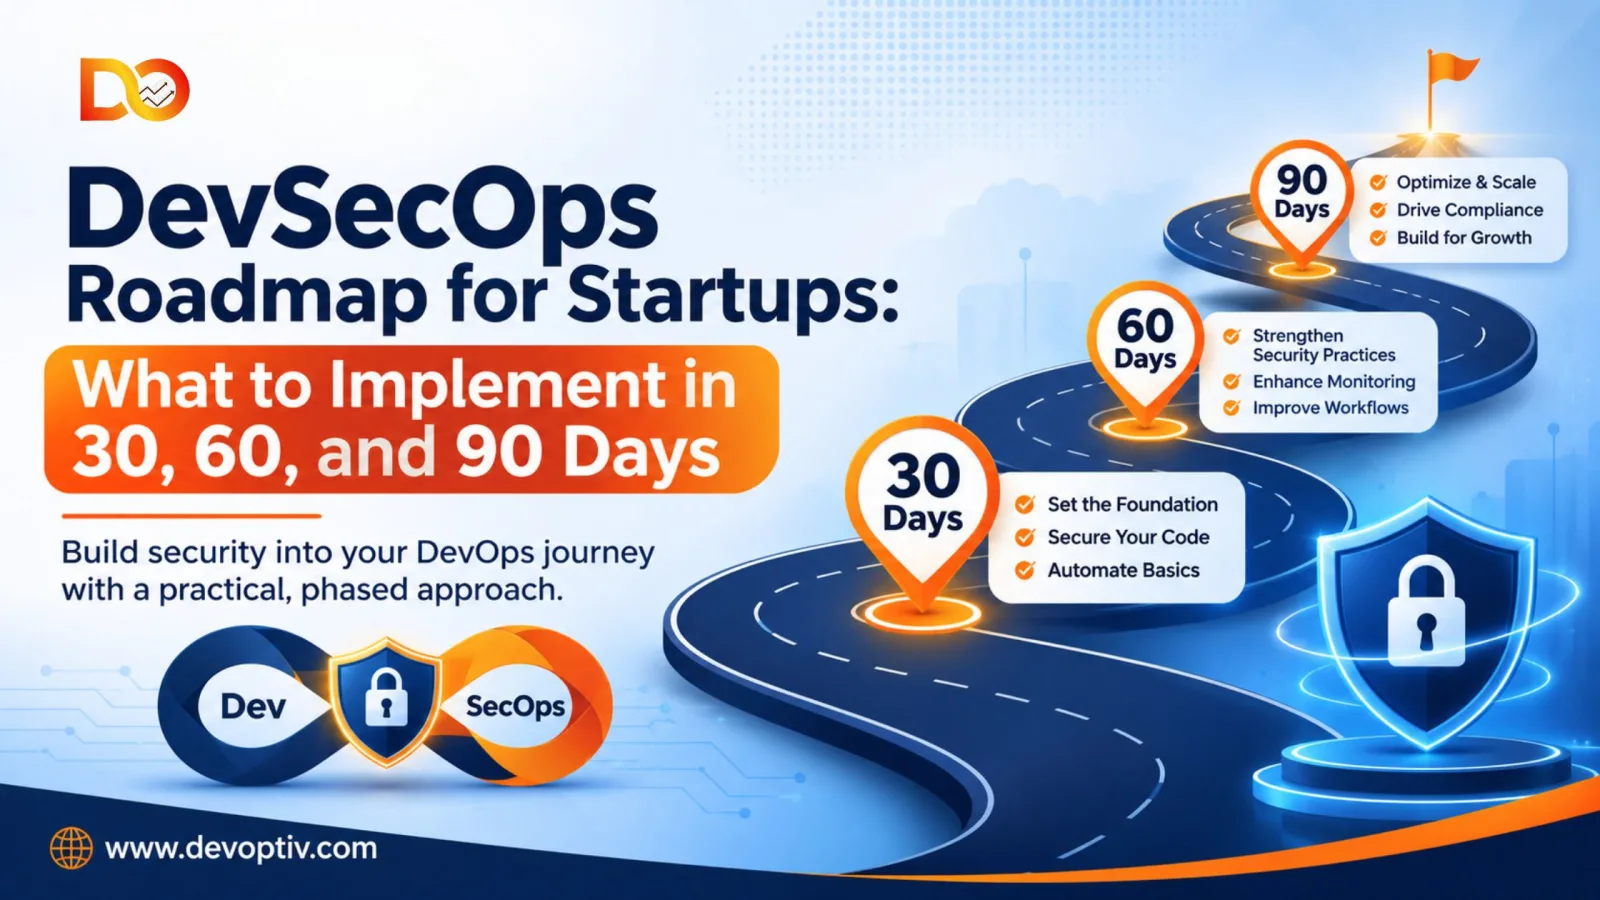
This guide lays out what effective DevSecOps services should deliver in your first 30, 60, and 90 days. It is written for founders, CTOs, and engineering leads who want a practical order of work, not a theory lecture.
DevSecOps means building security into every stage of software delivery: planning, coding, building, testing, deploying, and running. Whether you build the capability in-house, hire a DevSecOps services company, or choose DevSecOps managed services, the sequence below stays the same: fix the basics, automate the checks, then mature the program.
Why Startups Should Start DevSecOps Early
Security debt behaves like technical debt: it compounds. Choices about authentication, secrets, and cloud permissions are cheap to get right in month one and painful to rewrite in year two.
There are three practical reasons to start now rather than after your first incident:
- Sales and fundraising. Enterprise buyers and investors increasingly ask how you protect code and customer data. Repeatable, documented controls shorten those conversations.
- Speed. A scanner that runs inside the pipeline in minutes beats a manual review that blocks a release for days.
- Cost of change. A flaw caught while the code is still on a developer's branch takes minutes to fix. The same flaw found in production means incident response, customer communication, and rework.
Small teams also depend heavily on open-source packages and managed cloud services, so a single weak dependency or a loose permission can expose the whole product. A staged roadmap lets you reduce that risk without hiring a full security department.
Week 0: Take a Baseline Before the Clock Starts
You cannot improve what you have not mapped. Spend a few days answering four questions:
- What are we protecting? List customer data, source code, cloud accounts, and third-party integrations.
- Where does code travel? Sketch the path from a developer's laptop through the repository, CI/CD, and cloud environment to production.
- Who has access to what? Export the users and roles in your cloud provider, code host, and CI system.
- What do customers or regulators expect? Note any SOC 2, ISO 27001, HIPAA, or GDPR requirements on your horizon.
The output is a one-page map and a short list of obvious risks. This is also the stage where an outside DevSecOps assessment pays off, because a fresh pair of eyes spots gaps a busy team has stopped noticing.
Days 1–30: Build the Foundation
The goal of the first month is to close the highest-risk gaps with low-effort controls. Do not buy a pile of tools yet. Most early breaches trace back to weak access, exposed secrets, and unreviewed code, so start there.
- Enforce MFA everywhere. Require multi-factor authentication on your code host, cloud console, CI/CD system, and email. Add single sign-on where the budget allows.
- Apply least privilege. Remove unused accounts, retire shared admin logins, and give each person and service only the access it needs.
- Find and rotate secrets. Scan repositories and their history for hardcoded passwords, tokens, and keys. Rotate anything you find, then move credentials into a secrets manager.
- Protect your main branch. Require pull requests, at least one reviewer, and passing checks before merge.
- Turn on dependency alerts. Enable automated alerts for vulnerable packages and start an inventory of what your product depends on.
- Switch on cloud audit logging. Check for publicly exposed storage, enable encryption defaults, and keep logs somewhere developers cannot quietly delete them.
- Name a security champion. Pick one engineer per team to own security questions and attend a short monthly review.
- Write a one-page security policy. Cover how to report an issue, who responds, and how quickly.
Done when: every engineer uses MFA, no known secrets sit in code, the main branch cannot be changed without review, and you can see who accessed what in your cloud account.
Days 31–60: Automate Security in the Pipeline
Once the basics hold, move checks into CI/CD so security runs on every change without anyone remembering to ask. This is the core of most DevSecOps services, and it is where the "shift left" idea becomes real.
- Static analysis (SAST). Scan source code on each pull request to catch injection flaws, insecure patterns, and risky functions before merge.
- Software composition analysis (SCA). Check open-source dependencies for known vulnerabilities and license problems, and generate a software bill of materials (SBOM) for each release.
- Secret scanning in the pipeline. Add pre-commit hooks and CI checks so a leaked credential is blocked before it reaches the repository.
- Infrastructure as code scanning. Review Terraform, CloudFormation, or Kubernetes files for open ports, public buckets, and over-broad permissions before they deploy.
- Container image scanning. Scan base images and built images, and standardize on a small set of trusted base images.
- Dynamic testing (DAST). Run automated tests against a staging environment to find issues that only appear while the application is running, such as weak authentication or exposed endpoints.
- Threat modeling for key features. Pick your one or two riskiest features, such as payments or login, and map how an attacker might abuse them.
Tune before you enforce. Run new scanners in report-only mode for one to two weeks, remove noisy rules, and then set clear gates: block critical and high findings, warn on medium, and track the rest. Teams that skip tuning drown in alerts and start ignoring them.
Done when: every pull request triggers SAST, SCA, and secret checks; infrastructure and container scans run before deploy; and findings have an owner and a target fix time.
Days 61–90: Mature, Monitor, and Scale
The third month turns a set of tools into a program. You now watch what runs in production, practice your response, and prepare the evidence customers and auditors ask for.
- Runtime monitoring and alerting. Centralize logs, enable cloud threat detection, and route high-severity alerts to a person who will act on them.
- Incident response plan and a tabletop exercise. Write down who does what in the first hour of an incident, then rehearse it once with a realistic scenario.
- Independent penetration test. Commission a vulnerability assessment and penetration test (VAPT) of your main product to validate what automation cannot see, such as business-logic flaws.
- Vulnerability management workflow. Connect scanner findings to your ticketing system, set fix targets by severity, and record any risk you knowingly accept.
- Compliance mapping. Map your controls to the framework you need, such as SOC 2 or ISO 27001, and automate evidence collection from your pipeline and cloud account. Policy as code helps here.
- Supply chain hardening. Pin dependency versions, sign build artifacts where possible, and limit the permissions of CI/CD tokens and runners.
- Retrospective and next-quarter plan. Review what the numbers show, retire rules that created noise, and set the next three goals.
Done when: you can show a customer or auditor your controls and evidence in under a day, an incident drill has been completed, and your team fixes critical findings within an agreed window.
The 30-60-90 Day DevSecOps Roadmap at a Glance
Use this table as a quick checklist or as a slide for your next planning meeting.
Phase | Focus | Key actions | Outcome |
|---|---|---|---|
Week 0 | Baseline | Map assets, code flow, access, and compliance needs | One-page risk map |
Days 1–30 | Foundation | MFA, least privilege, secret scanning, branch protection, dependency alerts, audit logs | Basic hygiene and visibility |
Days 31–60 | Automation | SAST, SCA, IaC and container scanning, DAST, threat modeling, severity gates | Security checks on every change |
Days 61–90 | Maturity | Monitoring, incident drill, VAPT, vulnerability workflow, compliance mapping | Repeatable, auditable program |
Metrics That Show Your DevSecOps Program Is Working
Track a handful of numbers from day one so you can prove progress to your board and your customers. Measure the trend, not a perfect score.
Metric | What it tells you |
|---|---|
Mean time to remediate critical findings | How fast your team closes serious risk |
Share of repositories with SAST, SCA, and secret scanning enabled | Coverage of your automation |
Open critical and high findings over time | Whether risk is shrinking or growing |
Secrets detected in code per month | Whether developer habits are improving |
False-positive rate of security checks | Whether your tuning keeps developers' trust |
Deployment frequency and lead time | Whether security is slowing delivery or not |
Time to produce audit evidence | How ready you are for SOC 2, ISO 27001, or a customer review |
In-House Team vs DevSecOps Managed Services
Early-stage teams rarely have a dedicated security engineer, and hiring one takes months. That is why many startups turn to DevSecOps managed services for the first year, then decide what to bring in-house as they grow.
Factor | Build in-house | DevSecOps managed services |
|---|---|---|
Time to start | Months, including hiring | Weeks, with a ready process |
Expertise | Limited to your hires | A team with broad tool and cloud experience |
Cost pattern | Salaries, tools, and training | Predictable monthly or project fee |
Coverage | Depends on team size and on-call | Continuous monitoring and support |
Control | Full ownership | Shared, set by contract and access |
Best for | Larger teams with steady security workload | Lean teams that need results fast |
A hybrid model often works best. An external partner sets up the pipeline, tunes the tools, and runs monitoring, while your own security champions own decisions about product risk. Ask any provider how they will transfer knowledge so you are never locked in.
Common DevSecOps Mistakes Startups Should Avoid
- Buying tools before fixing basics. A scanner will not help if everyone shares an admin password.
- Turning on every rule at once. Flooding developers with thousands of alerts teaches them to ignore all of them.
- Treating security as one person's job. Without shared ownership, findings pile up in a backlog nobody reads.
- Chasing compliance paperwork instead of real controls. Auditors can tell the difference, and so can attackers.
- Skipping the human side. Short, relevant training and a friendly champion network do more than a long policy document.
- Never revisiting the plan. Your stack, team, and threats change every quarter, so review the roadmap on a schedule.
How to Choose a DevSecOps Services Company
If you decide to bring in outside help, judge providers on how they work, not on logos or tool lists. Ask these questions:
- Do they start with an assessment? A good partner reviews your stack and goals before proposing anything.
- Do they cover the full pipeline? Look for experience across SAST, SCA, DAST, IaC and container scanning, cloud security, and penetration testing.
- Will they fit your tools? The goal is to work inside your existing Git, CI/CD, and cloud setup, not to replace it.
- How do they handle alert noise? Ask how they tune rules and prioritize findings so developers keep moving.
- Can they support compliance? Check whether they help with SOC 2, ISO 27001, HIPAA, or GDPR evidence.
- What happens at the end? Insist on documentation, runbooks, and training so your team can take over.
- How do they report? Expect plain-language dashboards tied to the metrics above.
For reference, DevOptiv offers cloud, DevOps, and DevSecOps work alongside application security testing and managed security and IT support, which suits startups that want one partner across the pipeline. Whoever you pick, ask for a clear scope, timeline, and exit plan in writing.
Conclusion: Start Small, Automate Early, Improve Every Quarter
You do not need a large budget or a security department to protect a young product. Fix access and secrets in the first 30 days, automate checks in the next 30, and build monitoring, response, and compliance evidence in the final 30. Measure progress, tune what creates noise, and revisit the plan every quarter.
If you would rather have experienced help, the team at DevOptiv offers DevSecOps services and DevSecOps managed services for startups and growing companies. Share your current stack and goals, and you can map this roadmap to your own pipeline.
0 comments
Log in to leave a comment.
Be the first to comment.