
B2B Endpoint Security: How to Protect Business Devices From Cyber Threats
Learn how B2B endpoint security helps protect business devices from cyber threats with device, network, application, data, and browser security controls.
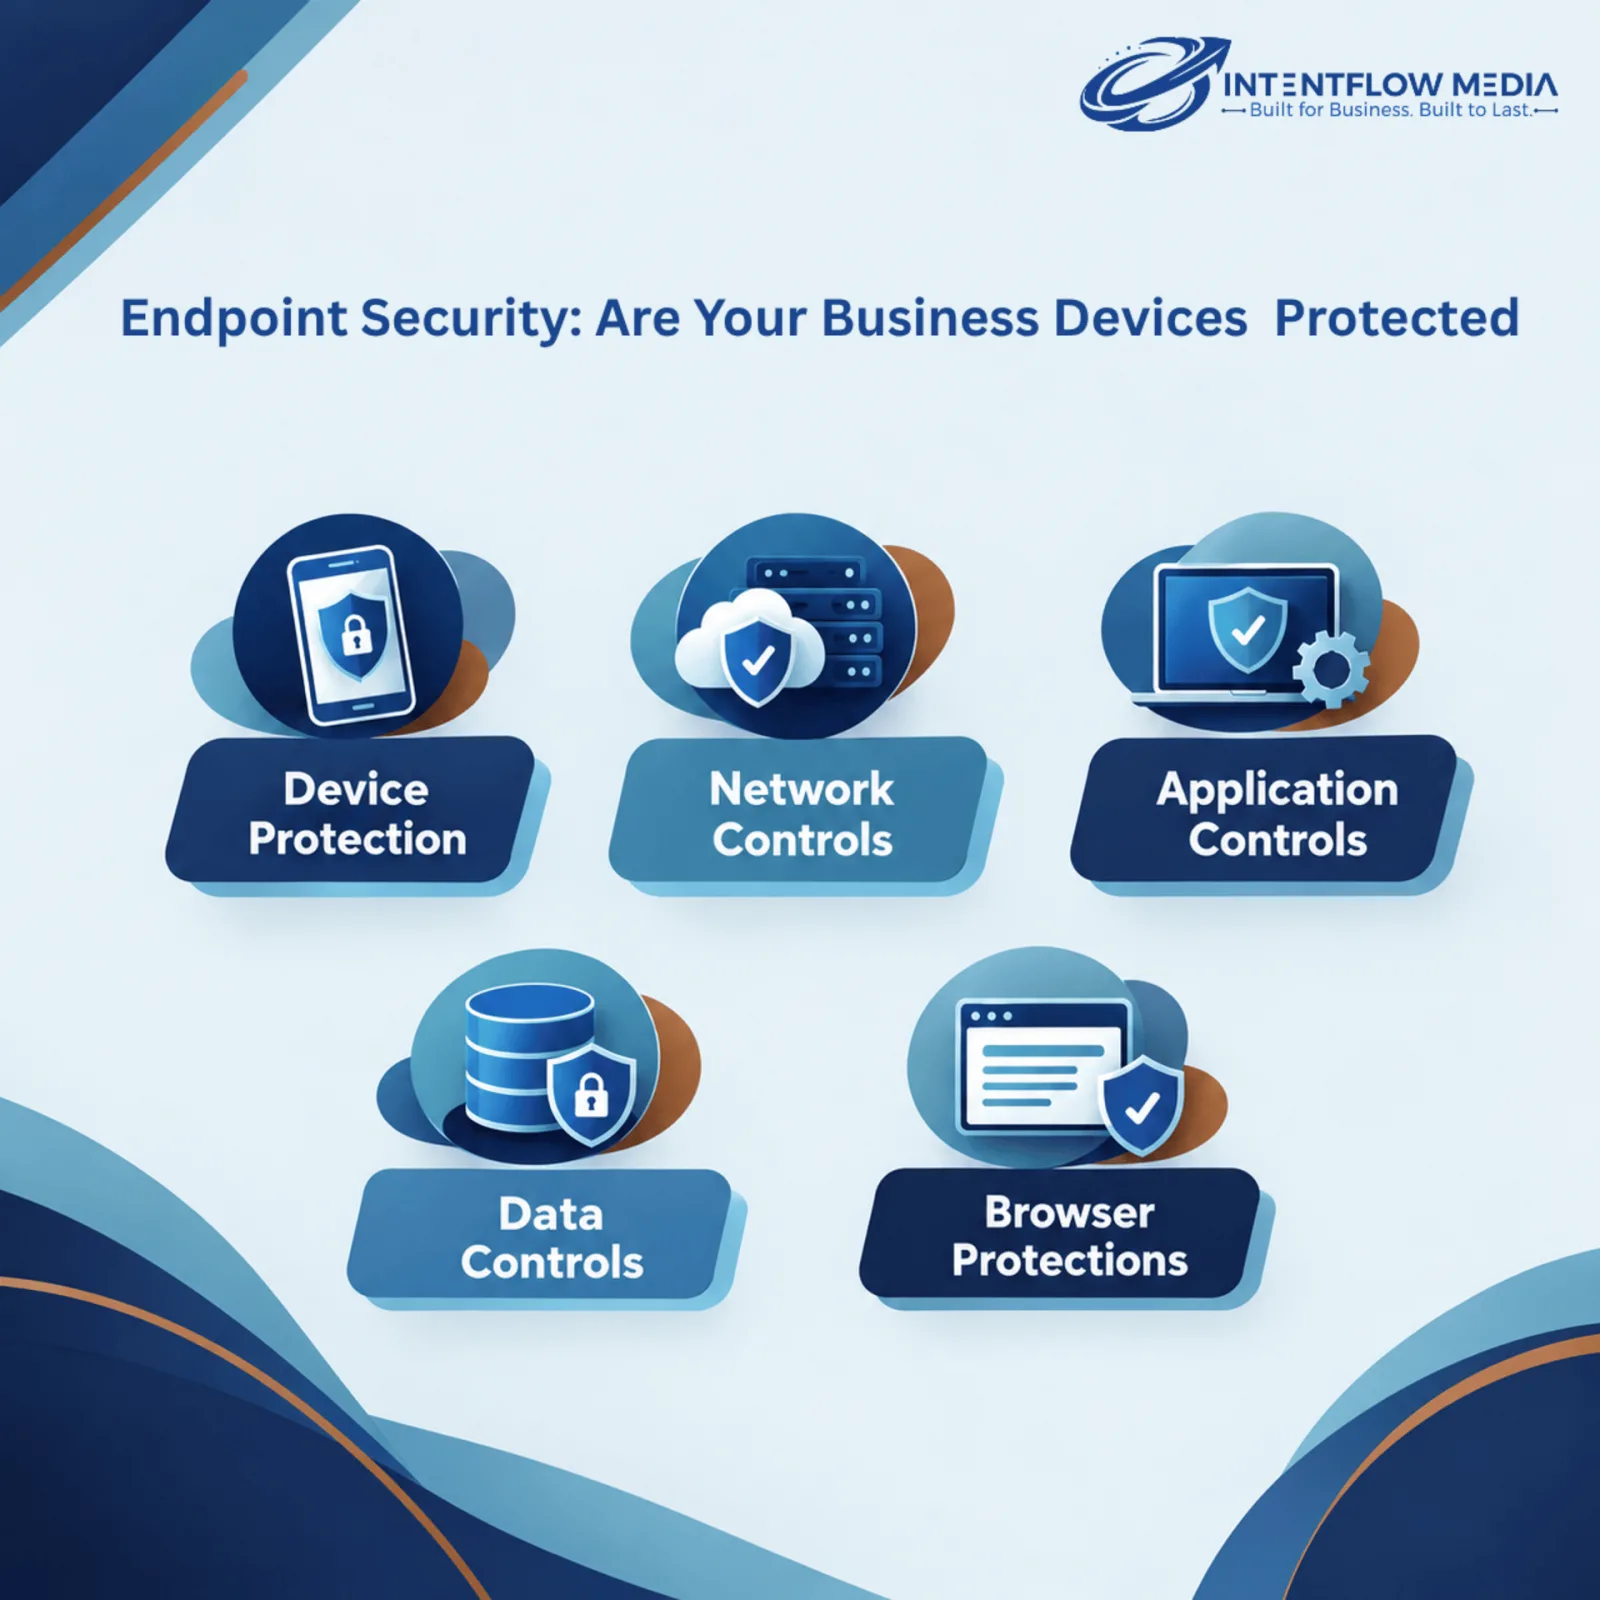
Introduction
An employee opens a fake Microsoft 365 login page on a company laptop. Their password is stolen, the attacker signs in, and suddenly the incident involves email, cloud applications, customer data, and internal systems.
This is why B2B endpoint security deserves attention beyond the IT department. The laptop was only the entry point.
For cybersecurity companies, reaching businesses with the right security needs also requires accurate email lead nurturing, useful sales-qualified leads, and focused B2B lead generation. The same businesses that need stronger endpoint protection are often dealing with remote employees, unmanaged devices, outdated software, and dozens of cloud applications.
The challenge is figuring out where those weaknesses exist and closing them before an attacker does.
What Is B2B Endpoint Security?
An endpoint is any device that connects to your company’s data or systems. This could include:
• laptops and PCs
• Mobile phones and tablets
• Servers of the company
• Remote operation equipment
• Point of sale terminals
• Associated business equipment
B2B endpoint security safeguards these devices from risks such as malware, ransomware, phishing attacks, credential theft, unsanctioned applications, and suspicious activities.
The item itself isn’t the only thing at risk.
A compromised laptop could contain browser sessions, saved credentials, business documents, VPN access, or connections to SaaS apps. An attacker who has control of that endpoint can exploit those rights to get access to other resources.
Why Business Endpoints Are Easy Targets
Employees engage with external websites, attachments, cloud applications, USB devices, and messaging systems on a daily basis.
That leaves room for attackers.
Let’s say you work in finance and receive an invoice attachment. The document seems authentic but launches a malicious script. The attacker then attempts to generate access or steal credentials to the machine.
The employee may not have done anything wrong.
This is why endpoint attacks are so hard to detect.
Common threats include:
Malware
Malicious software can steal information, corrupt data, monitor behavior, or give an attacker control of a device.
Ransomware
may cripple a firm by locking off files and stopping activities. If networked systems or shared storage are also compromised, then the recovery becomes far more difficult.
Phishing
A fake login page can capture usernames, passwords, or session information. Email isn't the only channel; attackers also use messaging platforms and compromised websites.
Credential theft
Stolen credentials can open access to email, cloud apps, VPNs, and other business systems.
Unpatched software
Old operating systems, browsers, VPN clients, and applications may contain vulnerabilities that attackers can exploit.
Unauthorized software
An employee installing an unapproved application or browser extension can introduce a security weakness that IT doesn't know about.
Start With an Accurate Device Inventory
You can't protect devices that aren't on your security team's radar.
A company may know it has 500 employees but still have no reliable answer to questions such as
- How many laptops are currently active?
- Which devices haven't checked in recently?
- Which machines are missing security software?
- Which operating systems are outdated?
- Which devices belong to former employees?
- Are contractors accessing company systems from unmanaged devices?
An endpoint inventory should record the device, assigned user, operating system, security agent status, patch status, encryption status, and recent activity.
This becomes especially important when employees work remotely.
Keep Software Patched
Security teams should have a clear process for identifying and fixing vulnerable software.
Prioritize patches based on factors such as:
- Severity of the vulnerability
- Whether the affected system is internet-facing
- Whether attackers are actively exploiting it
- How important the device or application is to business operations
Use EDR to Watch Endpoint Activity
Endpoint Detection and Response (EDR) looks beyond individual malicious files.
It records and analyzes activity on endpoints so security teams can investigate unusual behavior.
Imagine this sequence:
- A user opens an unexpected document.
- A script launches.
- The script starts another process.
- That process attempts to access several files.
- The device makes an unusual external connection.
Protect Remote and Hybrid Devices
Remote work changes where security incidents can begin.
A company laptop may connect from a home router on Monday, a hotel network on Wednesday, and a client office on Friday. The device still needs the same basic protections.
Businesses should consider:
- Full-disk encryption
- Multi-factor authentication
- Automatic security updates
- Endpoint monitoring
- Mobile-device management where applicable
- Strong device authentication
- Remote device lock or wipe capabilities
- Controls for company data on personal devices
Security policies should also explain what employees are allowed to do with company devices.
A two-page policy people understand is more useful than a 40-page document nobody reads.
Limit Administrative Access
Giving every employee administrator privilege can increase the damage caused by a compromised account.
If malware runs with administrative rights, it may have more freedom to modify system settings, install software, disable protections, or access sensitive areas.
Use the principle of least privilege instead.
Employees should have the permissions required for their work, while elevated access should be restricted and monitored.
This doesn't eliminate endpoint attacks, but it can reduce what an attacker can do after gaining access.
Control Applications and Browser Extensions
Free software isn't automatically safe.
An employee may install a PDF converter, password manager, browser extension, remote-access tool, or AI application without involving IT.
The application may be legitimate. The problem is that the company may have no idea what permissions it has or what information passes through it.
Application controls can help IT teams approve known software and block applications that create unnecessary risk.
Browser extensions deserve attention too. Some can access website content, browsing activity, or information entered into web applications.
Train Employees on Specific Threats
"Watch out for phishing" is too vague.
Give employees situations they can recognize.
For example:
A supplier emails your accounts team asking for bank details to be changed before the next payment.
The correct response isn't simply to inspect the email for spelling mistakes. The employee should verify the request through an established contact method before changing payment information.
The same principle applies to:
- Unexpected password-reset emails
- Fake software-update messages
- Unusual file-sharing invitations
- Requests for MFA codes
- Urgent requests from executives
- Unknown USB devices
Employees should also know exactly where to report suspicious activity.
Have an Endpoint Incident Response Plan
When a device is compromised, hesitation can make the situation worse.
A basic response process should cover:
1. Isolate the endpoint.
Remove the device from business networks where possible.
2. Preserve evidence
Security teams may need logs, processes, network connections, or other
information to understand the attack.
3. Investigate access
Check whether credentials, files, applications, or other endpoints were
affected.
4. Revoke compromised access
Reset passwords, terminate active sessions, and review authentication activity
when necessary.
5. Check other devices
Look for similar indicators elsewhere in the environment.
6. Recover the endpoint
Restore the machine using a trusted process rather than simply reconnecting it
after removing an obvious file.
7. Document the incident.
Record what happened, how it was detected, and what control needs to change.
That final step matters. Otherwise, the company may fix today's infected laptop and leave tomorrow's weakness untouched.
Common Endpoint Security Mistakes
A few problems appear repeatedly in business environments:
Treating antivirus as the whole solution
Antivirus is useful, but endpoint security also involves patching, access control, monitoring, encryption, application controls, and recovery.
Ignoring inactive devices
A laptop that hasn't checked in for 60 or 90 days shouldn't quietly remain in the inventory.
Giving excessive permissions
Unnecessary administrator rights can increase the impact of a compromised account.
Forgetting third-party devices
Contractors and partners may have access to company systems without being managed like employee devices.
Collecting alerts without reviewing them
Security tools generate information. Someone still needs to determine which events require investigation.
Having no recovery plan
If ransomware hits 20 machines at once, the company needs a tested recovery process—not a discussion about creating one.
A Practical Endpoint Security Checklist
Use these questions during a security review:
- Do we have an accurate inventory of every business endpoint?
- Are security agents active on all supported devices?
- Are critical vulnerabilities patched promptly?
- Are endpoints encrypted?
- Is MFA enabled for important business accounts?
- Do employees have unnecessary administrator access?
- Are remote devices monitored?
- Can IT isolate a compromised endpoint quickly?
- Are third-party devices covered by access policies?
- Can the company restore critical data after ransomware?
- Do employees know how to report suspicious activity?
- Has the incident-response process been tested?
If several answers are unclear, those gaps deserve attention before adding another security product.
FAQ
1. What is B2B endpoint security?
B2B endpoint security protects business devices such as laptops, desktops, smartphones, and servers from malware, unauthorized access, credential theft, ransomware, and other threats.
2. Is antivirus enough for business endpoint security?
No. Antivirus is one security layer. Businesses may also need EDR, patch management, encryption, access controls, MFA, application controls, backups, and incident-response procedures.
3. Why is EDR useful?
EDR monitors activity on endpoints and helps security teams investigate suspicious behavior. It can also support actions such as isolating affected devices during an incident.
4. How can companies secure remote employees?
Use managed devices where possible, keep software patched, enable MFA, encrypt devices, monitor endpoint activity, restrict unnecessary permissions, and provide clear security procedures.
5. What should a company do after an endpoint is compromised?
Isolate the affected device, investigate what happened, review credentials and access, check for other affected endpoints, recover the device safely, and document the incident.
Conclusion
A secure laptop is useful. A company that knows which devices it has, who can access them, what software is running, and what happens when something goes wrong is in a much stronger position.
For cybersecurity providers, reaching those businesses requires the same level of precision. ICP targeting helps identify companies with a genuine need, Sales-Qualified Leads provides context around their technology and buying roles, and focused B2B lead generation connects those businesses with relevant security solutions.
Endpoint security isn't about buying the longest list of security tools.
It starts with knowing your endpoints, limiting unnecessary access, watching for unusual behavior, patching known weaknesses, and having a response plan ready before an employee reports, "Something strange just happened on my laptop."
0 comments
Log in to leave a comment.
Be the first to comment.