
AI Compliance Software: A Practical Guide for Businesses Using Artificial Intelligence
Explore AI compliance software for managing AI inventory, risk, EU AI Act obligations, documentation, evidence, monitoring, and audit readiness.
Artificial intelligence is becoming part of everyday business operations. Companies use AI for customer service, recruitment, fraud detection, marketing, analytics, software development, content generation, and decision support. As these systems become more widespread, businesses also need better ways to understand and manage the risks associated with them.
This is where AI Compliance Software can become useful.
Instead of managing AI inventories, risk assessments, documentation, regulatory requirements, and evidence through disconnected spreadsheets and folders, businesses can use dedicated software to bring these activities into a structured workflow.
For organisations operating in Europe, this is particularly relevant as the EU AI Act introduces requirements that vary according to factors such as the AI system's intended purpose, risk classification, and the role of the organisation.
What Is AI Compliance Software?
AI Compliance Software is designed to help businesses manage regulatory and governance requirements associated with artificial intelligence.
A typical solution may help organisations:
Maintain an inventory of AI systems
Identify AI-related risks
Classify AI systems according to applicable requirements
Map regulatory obligations
Manage compliance documentation
Collect and organise evidence
Monitor AI systems over time
Prepare for audits
Assign responsibilities to internal teams
Track compliance activities
The exact capabilities differ between products. Some tools focus on general governance, risk, and compliance, while dedicated AI compliance platforms focus specifically on AI-related regulations and operational requirements.
For businesses with several AI systems, the ability to connect these activities can make compliance management more structured and easier to maintain.
Why Businesses Are Looking at AI Compliance Tools
AI governance can become complicated as organisations introduce more models, applications, APIs, and third-party AI services.
For example, a SaaS company may use one AI model for customer support, another for document analysis, and several third-party AI APIs within its product. Each system may have a different owner, purpose, data flow, and risk profile.
Maintaining this information manually can create gaps.
An AI compliance tool can provide a central location where organisations track their AI systems and connect each system to its relevant assessments, requirements, documents, and evidence.
This also helps businesses move away from a reactive approach to compliance.
Instead of collecting documents only when an auditor, customer, or regulator asks for them, teams can maintain records as part of their normal AI development and governance processes.
AI Compliance Software and the EU AI Act
The EU AI Act is an important consideration for businesses developing or deploying AI in Europe.
The regulation uses a risk-based framework, meaning that different AI systems can be subject to different requirements.
Factors such as the intended purpose of an AI system and the organisation's role can affect the obligations that need to be considered.
This makes EU AI Act compliance software useful for organisations that need to keep track of multiple systems.
A structured workflow can help teams connect an AI system with:
Its intended purpose
Its provider or deployer role
Its risk classification
Applicable regulatory obligations
Required documentation
Evidence and approvals
Ongoing monitoring activities
This approach can be especially useful for organisations developing AI products rather than simply experimenting with AI internally.
The Role of AI Risk Management
Risk assessment is one of the central elements of AI governance.
Businesses need to understand what their AI systems do, where they are deployed, who is affected by them, and which regulatory requirements may apply.
An AI risk management platform can help organise this process by providing structured assessments and maintaining records associated with each system.
For example, an organisation could maintain information about an AI recruitment application separately from an internal marketing assistant. The systems may use similar underlying technologies, but their purposes and compliance considerations can be very different.
A centralised risk management process makes it easier to review these systems individually while maintaining an organisation-wide view.
Documentation and Evidence Management
AI compliance is not only about identifying applicable rules. Organisations also need to maintain documentation and supporting evidence.
Depending on the system and regulatory requirements, this can involve technical documentation, risk assessments, impact assessments, policies, testing records, approvals, monitoring results, and other compliance records.
An AI governance platform can help organise these materials around individual AI systems.
This creates a clearer relationship between a requirement and the evidence supporting it.
For example, instead of storing an assessment in one folder and related approval emails somewhere else, a compliance workflow can associate the assessment, reviewer, approval, and supporting evidence with the relevant AI system.
This becomes particularly valuable when organisations need to prepare for an AI compliance audit.
AI Compliance and GDPR
AI governance can also overlap with data protection.
Many AI systems process personal data, while some may involve profiling, automated decision-making, or other activities that require privacy considerations.
The EU AI Act and GDPR are separate legal frameworks, but organisations may need to manage requirements from both when developing or deploying certain AI systems.
This is why some businesses are exploring GDPR and AI compliance software that can bring relevant governance activities together while keeping the requirements of each regulation distinct.
A connected workflow can help teams coordinate areas such as:
Data governance
AI risk assessments
Privacy impact assessments
Documentation
Accountability
Human oversight
Monitoring
Review and approval processes
The objective is not to treat GDPR and AI Act compliance as the same process, but to identify where the operational workflows overlap.
Features to Consider When Choosing AI Compliance Software
Businesses evaluating AI compliance solutions should look beyond the appearance of a dashboard.
The more important question is whether the software supports the organisation's actual governance workflow.
AI Inventory
The software should provide a structured way to identify and manage AI systems across departments.
Risk Classification
A useful platform should help teams assess the regulatory position of individual AI systems rather than treating the entire organisation as having one compliance status.
Obligation Management
Teams should be able to connect applicable requirements with the relevant AI systems, owners, and activities.
Documentation Management
The platform should help organisations create, manage, review, and maintain relevant compliance documentation.
Evidence Management
Evidence should remain connected to the requirements and systems it supports. Approval workflows and audit trails can also help improve traceability.
Continuous Monitoring
AI systems can change after their initial assessment. Monitoring capabilities can help organisations identify changes that may require additional review.
Integrations
Integration with development and business tools can make compliance part of existing workflows instead of creating another isolated system.
AI Compliance for SaaS Companies and Startups
SaaS companies often have AI distributed across their products and internal operations.
An AI-powered feature may be developed by engineering, managed by a product team, reviewed by legal, and ultimately used by customers across several markets.
For an AI startup, the situation can be similar. Teams often need to move quickly while establishing governance processes at the same time.
Dedicated AI compliance automation can help create repeatable processes around system discovery, risk classification, documentation, evidence collection, and monitoring.
The objective is not to automate every compliance decision.
Instead, automation can handle structured and repetitive activities while giving legal, compliance, privacy, security, and technical teams the information they need to review important decisions.
Turning Compliance Into an Ongoing Process
One of the biggest challenges in AI governance is that compliance is not necessarily a one-time exercise.
A model can be updated. A vendor can change its service. A new AI feature can be added to an existing product. An organisation can expand into another market.
Any of these changes can affect the information previously recorded about an AI system.
This makes continuous AI compliance an important concept for organisations with growing AI portfolios.
A practical workflow can follow a simple cycle:
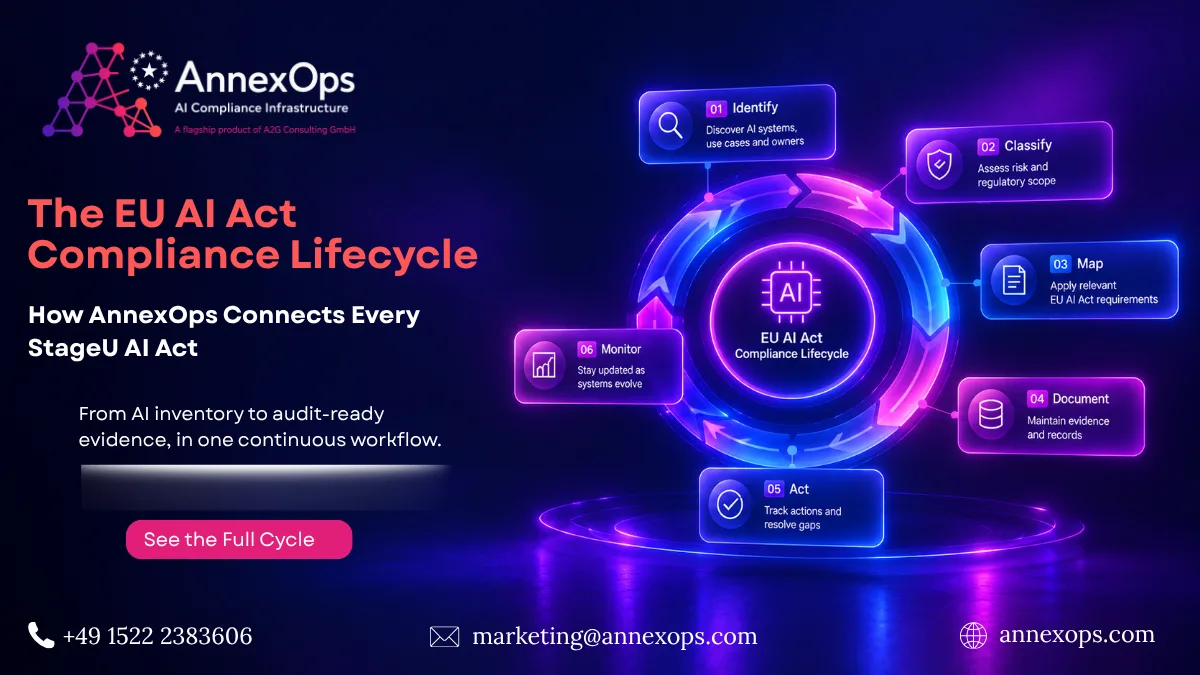
Discover → Assess → Classify → Map obligations → Document → Collect evidence → Monitor → Review
When these activities are connected, organisations can maintain a clearer picture of their AI environment and respond more efficiently when systems change.
Choosing an AI Compliance Platform
There is no single approach that works for every organisation.
A company with two experimental AI tools may have different requirements from an enterprise managing hundreds of AI systems across multiple departments.
Before selecting an AI compliance platform, organisations should consider:
How many AI systems they currently manage
Whether they develop or deploy AI products
Which regulations apply to their operations
How risk assessments are currently performed
Where compliance evidence is stored
Whether legal and technical teams need shared workflows
Which development or business systems need integrations
How frequently AI systems change
What audit and reporting requirements exist
These questions can help businesses identify whether they need general GRC functionality, specialised AI governance capabilities, or a combination of both.
Building a More Structured AI Governance Process
As AI becomes more deeply integrated into business operations, compliance needs to keep pace with technology.
Spreadsheets and shared folders may work at an early stage, but they can become harder to manage as the number of AI systems, stakeholders, requirements, and evidence records increases.
AI Compliance Software provides a way to structure these activities around the AI systems an organisation actually uses.
Platforms such as AnnexOps are designed to support AI governance workflows covering areas such as AI discovery, risk classification, obligation management, documentation, evidence, monitoring, and audit readiness.
The broader goal is simple: make AI compliance part of the operating process rather than something handled separately when a deadline or audit approaches.
For organisations building or deploying AI in Europe, establishing this kind of structured process can help teams maintain better visibility over their AI portfolio and understand what needs attention as their systems evolve.
0 comments
Log in to leave a comment.
Be the first to comment.