
AI Agent Security: Risks and Best Practices for Business Adoption
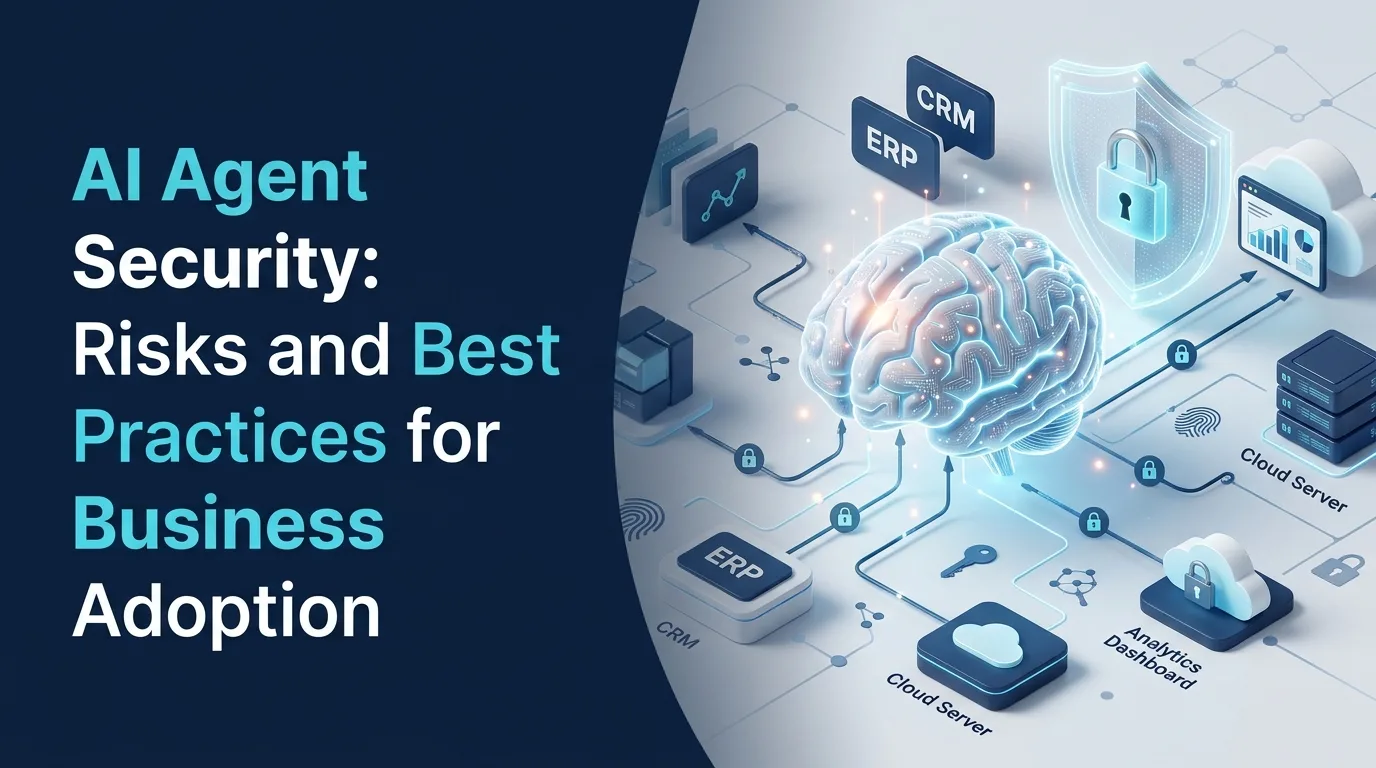
AI Agents Are Becoming Part of Everyday Business Operations. They Can Handle Customer Requests, Process Information, Manage Workflows and Support Decisions With Less Human Involvement. However, Giving AI Agents Access to Business Systems and Sensitive Data Also Creates Security Risks. Companies Need Clear Security Measures Before Using These Tools in Real Business Environments. A Strong Approach Helps Businesses Gain the Benefits of AI While Keeping Their Data and Operations Protected.
Why AI Agent Security Matters
Unlike traditional software that follows fixed instructions, AI agents can interpret information and take actions based on their goals. Depending on their permissions, they may access files, call APIs, update records or interact with other applications. This makes them useful for complex tasks but increases the impact of mistakes and security attacks.
IBM's 2025 Cost of a Data Breach Report found that the global average cost of a data breach reached $4.44 million. This figure shows the financial impact of security failures. As businesses connect AI agents to internal systems, they must consider how an agent could expose confidential information or perform an action without proper approval.
Common Security Risks in AI Agents
Unauthorized Access to Business Data
AI agents may need access to customer records, internal documents or financial information to complete tasks. If permissions are too broad, an agent could retrieve data that is unnecessary for its work. Poor access controls can also increase the risk of sensitive information being exposed to the wrong users.
Prompt Injection Attacks
Prompt injection occurs when malicious instructions are placed inside content an AI agent reads. These instructions may appear in emails, documents or web pages. If the agent follows them instead of its intended rules, it could reveal information or perform unwanted actions. This risk becomes more serious when agents can use external tools.
Uncontrolled Actions
An AI agent may misunderstand a request or produce an incorrect result. If it can approve payments, change customer records or send messages without review, a small error could create a larger business problem. The risk grows when multiple agents or systems depend on the same output.
Weak Monitoring and Accountability
Some businesses may struggle to understand why an agent took a particular action. Without detailed logs and clear ownership, investigating an incident becomes harder. Security teams need visibility into agent activity so they can identify unusual behavior and respond quickly.
Best Practices for Secure AI Agent Adoption
Apply Least-Privilege Access
Give each agent only the permissions required for its assigned tasks. Separate access to sensitive systems and review permissions regularly. Avoid using shared administrator accounts for automated workflows.
Keep Human Approval for High-Risk Actions
Require human approval before an agent makes major financial changes, deletes important records or shares sensitive information. Low-risk tasks can run automatically when appropriate safeguards are in place. This approach supports efficiency without removing essential oversight.
Test Against Realistic Threats
Security testing should include prompt injection, unauthorized data requests and attempts to misuse connected tools. Test agents in controlled environments before deployment. Repeat these tests whenever models, permissions, integrations or workflows change.
Monitor Activity and Set Clear Limits
Maintain logs of agent decisions and tool usage. Set limits on what agents can access and how many actions they can perform. Alerts can help security teams detect unusual activity. Businesses should also have a way to pause or disable an agent when something goes wrong.
Protect Data Throughout the Workflow
Use encryption where appropriate and follow established data retention policies. Avoid sending confidential information to systems that have not been approved for business use. Review vendor security practices and confirm how data is stored and processed.
Building Security Into AI Agent Development
Security should be part of the design process rather than a final checkpoint. Businesses investing in AI Agent Development Services should assess identity controls, data access, testing, monitoring and recovery procedures from the beginning. Development teams should also document agent permissions and define which actions require human review.
A secure deployment needs ongoing maintenance. Threats change over time and business workflows evolve. Regular reviews help organizations identify gaps before they become serious incidents.
Conclusion
AI agents can help businesses work faster and manage complex tasks. However, adoption must come with clear rules for access, oversight and accountability. Start with limited permissions and test each agent before expanding its responsibilities. Monitor activity and review security controls as systems change. Tech.us encourages businesses to treat AI agent security as an ongoing responsibility so they can adopt intelligent automation with greater confidence.
0 comments
Log in to leave a comment.
Be the first to comment.